
Assess Your Cybersecurity Insurance Policy
Adapt to changes in the cyber insurance market.
The cyber insurance market continues to evolve as emerging risks, including those associated with AI, affect the cost, availability, and scope of coverage. Insurer requirements have steadily risen and now include more detailed questionnaires, mandatory security controls, and stricter policy language. As the list of expected controls grows, organizations may struggle to determine which ones to prioritize. This research provides a structured methodology and practical tools to help organizations understand their risk exposure, determine appropriate coverage, strengthen control readiness, and evaluate whether a cyber insurance policy meets their needs.
Treating cyber insurance as a simple way to transfer risk can lead organizations to underestimate the role mature security controls play in obtaining and maintaining coverage. Insurance is most effective when considered as one component of a broader, risk-informed approach to cybersecurity, supported by a clear understanding of organizational needs, policy options, and available market expertise.
- The cyber insurance market continues to evolve.
- Connect with an insurance broker.
- Advancing program maturity will be necessary.
Though premiums have stabilized and, in some cases, decreased, cyber insurance requirements continue to evolve alongside the threat landscape. Proactively monitoring cyber risk and maintaining an adaptive security posture can help organizations keep pace with changes in coverage, insurer expectations, and costs.
An insurance broker can help organizations navigate the cyber insurance market, especially when comparing policies from different insurers. Brokers provide industry-specific benchmarks on pricing, coverage, clauses, and other key terms and conditions while helping organizations interpret differences in policy language.
Organizations should continually improve their information security program, regardless of whether they intend to obtain cyber insurance. A mature security program aligned with the organization’s threat profile and backed by a risk-informed approach can improve insurability, providing greater confidence that a policy will pay out when it matters.
Use this research to develop your cyber insurance strategy.
This research helps IT leaders understand their organization’s risk management needs and determine an appropriate approach to cyber insurance. The three-phase methodology is supported by practical tools and templates that help organizations complete key activities, develop actionable outputs, and make informed decisions about their cyber insurance strategy.
Follow the three-phase approach to:
- Assess your organization’s threat landscape and estimate remediation costs to determine coverage needs.
- Validate security control readiness, navigate common insurance pitfalls, evaluate policy elements, and negotiate and purchase coverage.
- Reassess policy suitability as coverage and premiums change and explore alternatives to cyber insurance.

On Demand
Webinar

Avoid Common Cyber Insurance Pitfalls
Play WebinarMember Testimonials
After each Info-Tech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve. See our top member experiences for this blueprint and what our clients have to say.
9.4/10
Overall Impact
$6,019
Average $ Saved
5
Average Days Saved
Client
Experience
Impact
$ Saved
Days Saved
Corporation Of The City Of Orillia
Guided Implementation
10/10
$10,000
5
No worst parts. He went above and beyond to help me and followup
Amerilife Group, LLC
Guided Implementation
10/10
N/A
10
Member Organization
Guided Implementation
10/10
$5,519
2
The details of his review was presented in a way very easy to consume. I also felt he had a very good understanding of the subject matter.
Member Organization
Guided Implementation
10/10
N/A
N/A
A very good initial discussion that helped shape the next steps for me.
Member Organization
Guided Implementation
10/10
$4,080
10
Best experience talking through the analysis and great feedback.
Member Organization
Guided Implementation
8/10
N/A
1
Member Organization
Guided Implementation
8/10
$10,000
2
Member Organization
Guided Implementation
10/10
$12,999
10
Michel was organized, helpful, and informative. He gave us items to consider that may save us money. He shared his experience with us. He gave us a... Read More
Member Organization
Guided Implementation
9/10
$12,599
20
Only a good experience!
Member Organization
Guided Implementation
10/10
$2,000
5
Member Organization
Guided Implementation
9/10
$71,499
2
Member Organization
Guided Implementation
9/10
N/A
N/A
Very helpful and achieved our goal of assisting in making the decision about what is next. Thanks Logan!
Member Organization
Guided Implementation
9/10
N/A
2
Not sure on savings just yet
Member Organization
Guided Implementation
9/10
N/A
5
Really appreciated the information and presentation of the information!
Member Organization
Guided Implementation
10/10
$5,039
5
Member Organization
Guided Implementation
9/10
$100K
10
Was able to chat on directionally how to progress next. Feedback on policy was very detailed that we can take to discussions with legal and the in... Read More
Member Organization
Guided Implementation
7/10
N/A
1
Logan provided some good information on what should included in cybersecurity insurance and send more information for reference.
On Demand
Webinar
Avoid Common Cyber Insurance Pitfalls
Play Webinar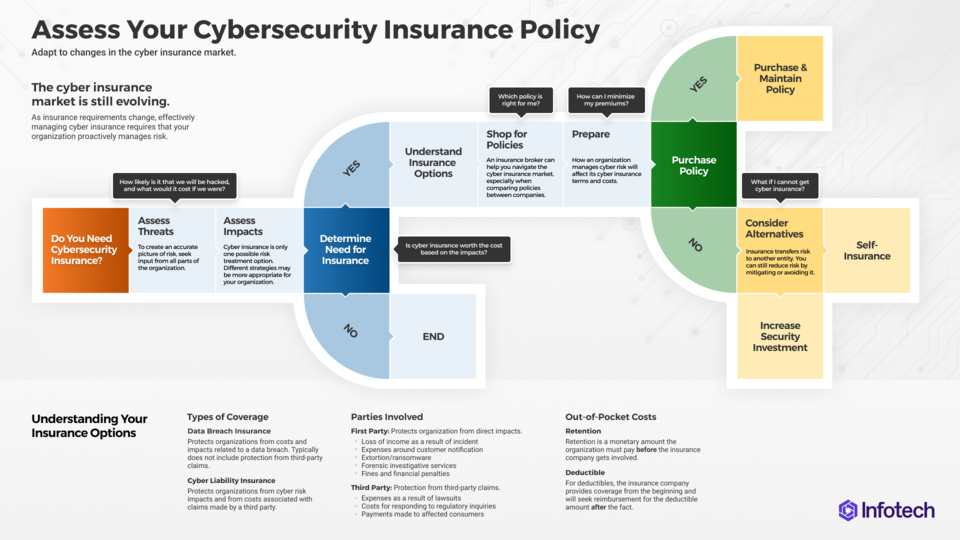
About Info-Tech
Info-Tech Research Group is the world’s fastest-growing information technology research and advisory company, proudly serving over 30,000 IT professionals.
We produce unbiased and highly relevant research to help CIOs and IT leaders make strategic, timely, and well-informed decisions. We partner closely with IT teams to provide everything they need, from actionable tools to analyst guidance, ensuring they deliver measurable results for their organizations.
What Is a Blueprint?
A blueprint is designed to be a roadmap, containing a methodology and the tools and templates you need to solve your IT problems.
Each blueprint can be accompanied by a Guided Implementation that provides you access to our world-class analysts to help you get through the project.
Need Extra Help?
Speak With An Analyst
Get the help you need in this 3-phase advisory process. You'll receive multiple touchpoints with our researchers, all included in your membership.
Guided Implementation 1: Gather requirements
- Call 1: Discuss insurance needs.
- Call 2: Review remediation cost estimates.
Guided Implementation 2: Procure policy
- Call 1: Discuss insurance pitfalls and strategies for success.
- Call 2: Review policy assessment.
Guided Implementation 3: Review
- Call 1: Determine policy review cadence.
Contributors
- Darren Brooks - Business Unit Head for Global Compliance Practice at ColorTokens, Inc.
- Ayhan Tek - Vice President, Information Security at Cyber Electra
- Kyle Gray - Cyber Insurance Educator and Underwriter at Ridge Canada Cyber Solutions Inc.
- Valerie Craig, Information Program Officer, Jones Capital
- John Armstrong, Chief Officer for Technology and Innovation, Joliet Public Schools District 86
- 2 anonymous contributors
 Assess and Manage Security Risks
 Assess Your Cybersecurity Insurance Policy
 Achieve Digital Resilience by Managing Digital Risk
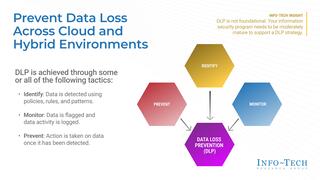 Prevent Data Loss Across Cloud and Hybrid Environments
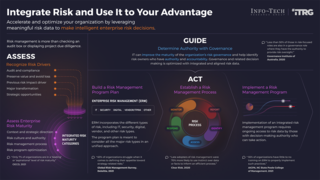 Build an IT Risk Management Program
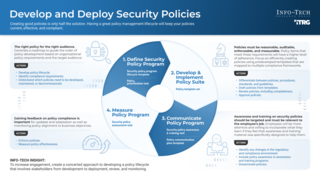 Develop and Deploy Security Policies
 Fast Track Your GDPR Compliance Efforts
 Build a Security Compliance Program
 Embed Privacy and Security Culture Within Your Organization
 Establish Effective Security Governance & Management
 Improve Security Governance With a Security Steering Committee
 Develop Necessary Documentation for GDPR Compliance
 Reduce and Manage Your Organization’s Insider Threat Risk
 Satisfy Customer Requirements for Information Security
 Master M&A Cybersecurity Due Diligence
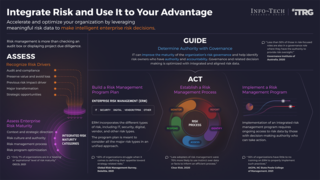 Integrate IT Risk Into Enterprise Risk
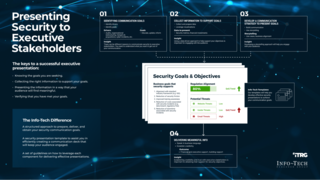 Present Security to Executive Stakeholders
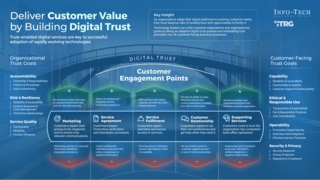 Deliver Customer Value by Building Digital Trust
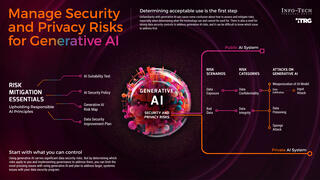 Address Security and Privacy Risks for Generative AI
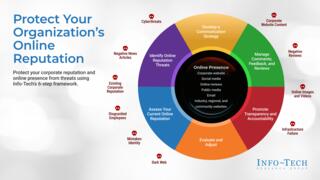 Protect Your Organization's Online Reputation
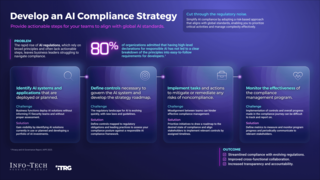 Develop an AI Compliance Strategy
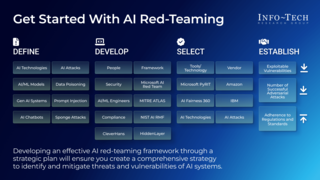 Get Started With AI Red-Teaming
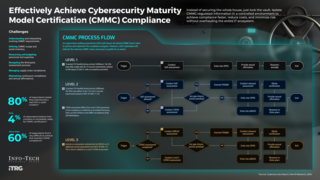 Achieve CMMC Compliance Effectively
 Building Info-Tech’s Chatbot
 Building the Road to Governing Digital Intelligence
 An Operational Framework for Rolling Out AI
 Discover and Classify Your Data
 Defend Against Deepfake Cyberattacks
 Assess Your CMMC Readiness
