
Build Security Services for Business Value
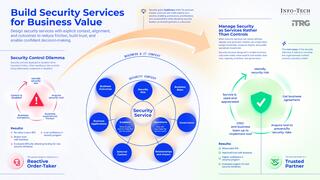
Design security services with explicit context, alignment, and outcomes to reduce friction, build trust, and enable confident decision-making.
Security leaders often respond to emerging threats by implementing tools or controls without fully understanding the context in which they must operate. As a result, those tools may fail to support the organizational outcomes they are meant to enable. When security is treated as a set of controls to be imposed – rather than services to be designed – IT leaders often struggle to explain its value, justify its cost, or gain support because those controls were never designed to work with how the organization delivers outcomes. Our research provides a structured approach that supports a fundamental shift in how security is viewed and implemented. Use this step-by-step framework to define, align, and operationalize security services within business services to support organizational outcomes.
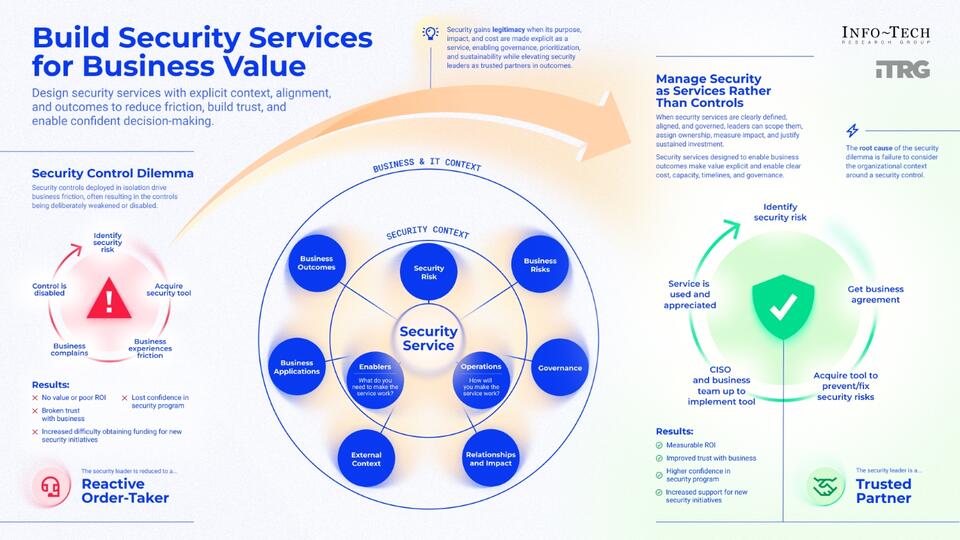
Too often, security is added to services rather than designed as part of them. Controls introduced without a deep understanding of the business can create friction, slow delivery, and force workarounds. Our research shows that security controls account for up to 56% of operational friction. Over time, this sustained friction erodes trust, makes funding difficult to defend, and can reduce the security leader role to that of a reactive order-taker.
1. Understand your service’s value and purpose.
Security gains legitimacy when its purpose, impact, and cost are made explicit as a service rather than a control. This enables governance, prioritization, and sustainability while elevating security leaders as trusted partners. When security decisions are grounded in shared context, leaders can clearly see what they are being asked to support, why it matters, and what trade-offs are involved.
2. Support organizational outcomes with design.
Security services are much more than isolated controls. They are supporting services, embedded within business services, that enable organizational outcomes. Integrated security services that facilitate organizational outcomes remain usable, beneficial, and willingly adopted.
3. Promote and champion your service’s benefits and needs.
Business leaders support what they understand. Communicate and market clear work, risks, needs, and costs so leaders can confidently prioritize and fund your security service. When the story resonates, services get prioritized, funded, and used as intended.
Use this step-by-step blueprint to design security services aligned to business outcomes.
Our research offers a step-by-step framework, along with practical templates and tools including a comprehensive workbook, communication template, and roadmap tool, to help you design security services with clear context, alignment, and outcomes. Use our phased approach to:
- Define service context to clarify purpose, scope, stakeholders, dependencies, risks, and organizational value.
- Align security with business services to show how security fits into workflows, reduces friction, and supports outcomes.
- Articulate shared success by defining measurable outcomes for both security and the organization.
- Translate service insight into a fundable, governable plan that produces clear narratives, cost estimates, resource requirements, and benefits aligned with decision-maker expectations.
Member Testimonials
After each Info-Tech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve. See our top member experiences for this blueprint and what our clients have to say.
10.0/10
Overall Impact
4
Average Days Saved
Client
Experience
Impact
$ Saved
Days Saved
Arkansas Research and Education Optical Network
Guided Implementation
10/10
N/A
4
Build Security Services for Business Value
Design security services with explicit context, alignment, and outcomes to reduce friction, build trust, and enable confident decision‑making.
Analyst perspective
Your security program isn’t underfunded; it is underdesigned.
Effective security is not enforced; it is designed. When security is treated as a set of controls to be imposed, leaders often struggle to explain its value, justify its cost, or gain sustained support, not because the business rejects security but because those controls were never designed to work with how the business actually delivers outcomes.
Too often, security is added to services rather than designed as part of them. Controls introduced without a deep understanding of the business service they support create friction, slow delivery, and force workarounds. Over time, trust erodes, funding becomes difficult to defend, and the security leader is reduced to a reactive order‑taker.
High‑performing organizations take a different approach. They treat security controls as services with clear ownership, defined outcomes, and continuous improvement. More importantly, they recognize security services as supporting services that collectively enable broader business services. This integration ensures security is designed to work with the flow of value, not against it.
When security is aligned to business outcomes, friction is reduced by design, adoption improves, and security outcomes are actually realized. Conversations shift from controls and compliance to enablement and value, elevating the security leader from enforcer to trusted business partner.
Diana MacPherson
Research Director, CIO
Info-Tech Research Group
Executive summary
Your Challenge
Security leaders often respond to emerging threats by implementing tools or controls without fully understanding the context in which those controls must operate.
- Tools are deployed to “fix a risk,” but the purpose, value, beneficiaries, and business impact are rarely defined.
- Security decisions occur in isolation from business outcomes, service interdependencies, or operational realities.
- As a result, controls become bolt‑ons that disrupt workflows rather than support them.
Impact: Friction, resistance, workarounds, and avoidance ultimately weaken the organization’s security posture and marginalize the security leader.
Common Obstacles
Security organizations struggle because of entrenched habits and structural gaps.
- Controls-first mindset: Security is treated as a collection of controls rather than a set of supporting services delivered to the business.
- Lack of service context: Security work is not defined in terms of who it affects, what business capabilities it enables, or what value it contributes.
- Misalignment with business services: Security functions rarely map their work to the business services they support, leaving expectations, effort, and outcomes unclear.
Impact: Without clear context and alignment, leaders cannot articulate purpose and value or confidently justify resources, costs, and timelines.
Info-Tech’s Approach
The better approach is to treat security controls as services:
- Define service context clearly: Clarify purpose, scope, stakeholders, dependencies, risks, and business value.
- Align with business services: Show how security fits into workflows, reduces friction, and supports outcomes.
- Articulate shared success: Define measurable outcomes for both security and the business.
- Translate service insight into a fundable, governable plan: Produce clear narratives, cost estimates, resource requirements, and benefits aligned to decision‑maker expectations.
Impact: Organizations secure long‑term investment and sustainability, and security leaders earn their place as trusted business partners.
Info-Tech Insight
Security gains legitimacy when its purpose, impact, and cost are made explicit as a service. This enables security leaders to move from enforcing controls to enabling business outcomes as trusted partners.
Security leaders must recognize that security controls never operate in isolation
Security often feels underfunded or unsupported, not because the work lacks importance, but because traditional, control‑centric approaches focus on enforcing safeguards rather than enabling business outcomes.
When controls are introduced without context, alignment, or clearly defined results, they create friction and workarounds that obscure their purpose and value and position security as a barrier rather than a business enabler. Business leaders rarely prioritize services that appear purposeless or that hinder their ability to achieve outcomes.
Why this matters now: Modern organizations need security designed to enable business outcomes, not obstruct them. Rising complexity, accelerating threats, and increasing dependence on digital operations mean security must shift to a service‑centric model grounded in clarity, legitimacy, and long‑term sustainability.
Only half of security leaders say their security organization works with business stakeholders.
51%
Source: Global Cyber Alliance, 2020
Security will gain legitimacy, prioritization, and funding if it overcomes these barriers:
- Treating security controls as bolt-ons. When security is treated as a bolt‑on rather than a service, friction and workarounds follow. The result is a weaker security posture and growing difficulty for leaders to justify investment, priority, and ownership.
- Failing to articulate purpose and value in business terms. If organizational leaders cannot see how a security service enables their outcomes, it becomes easy to deprioritize, underfund, or overlook. Security cannot reduce risk without the backing of the business.
By leading with context, alignment, and measurable impact, security leaders can end the cycle of friction and avoidance that increases organizational risk rather than reduces it.
Security teams that act as trusted business enablers are more likely to secure funding and attract top talent.
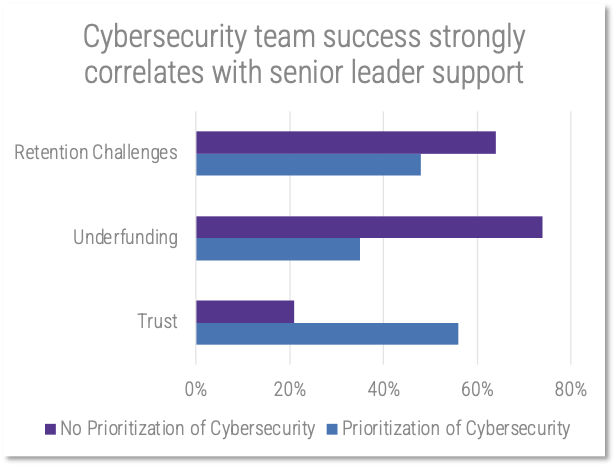
Source: ISACA, 2025
Info-Tech’s approach
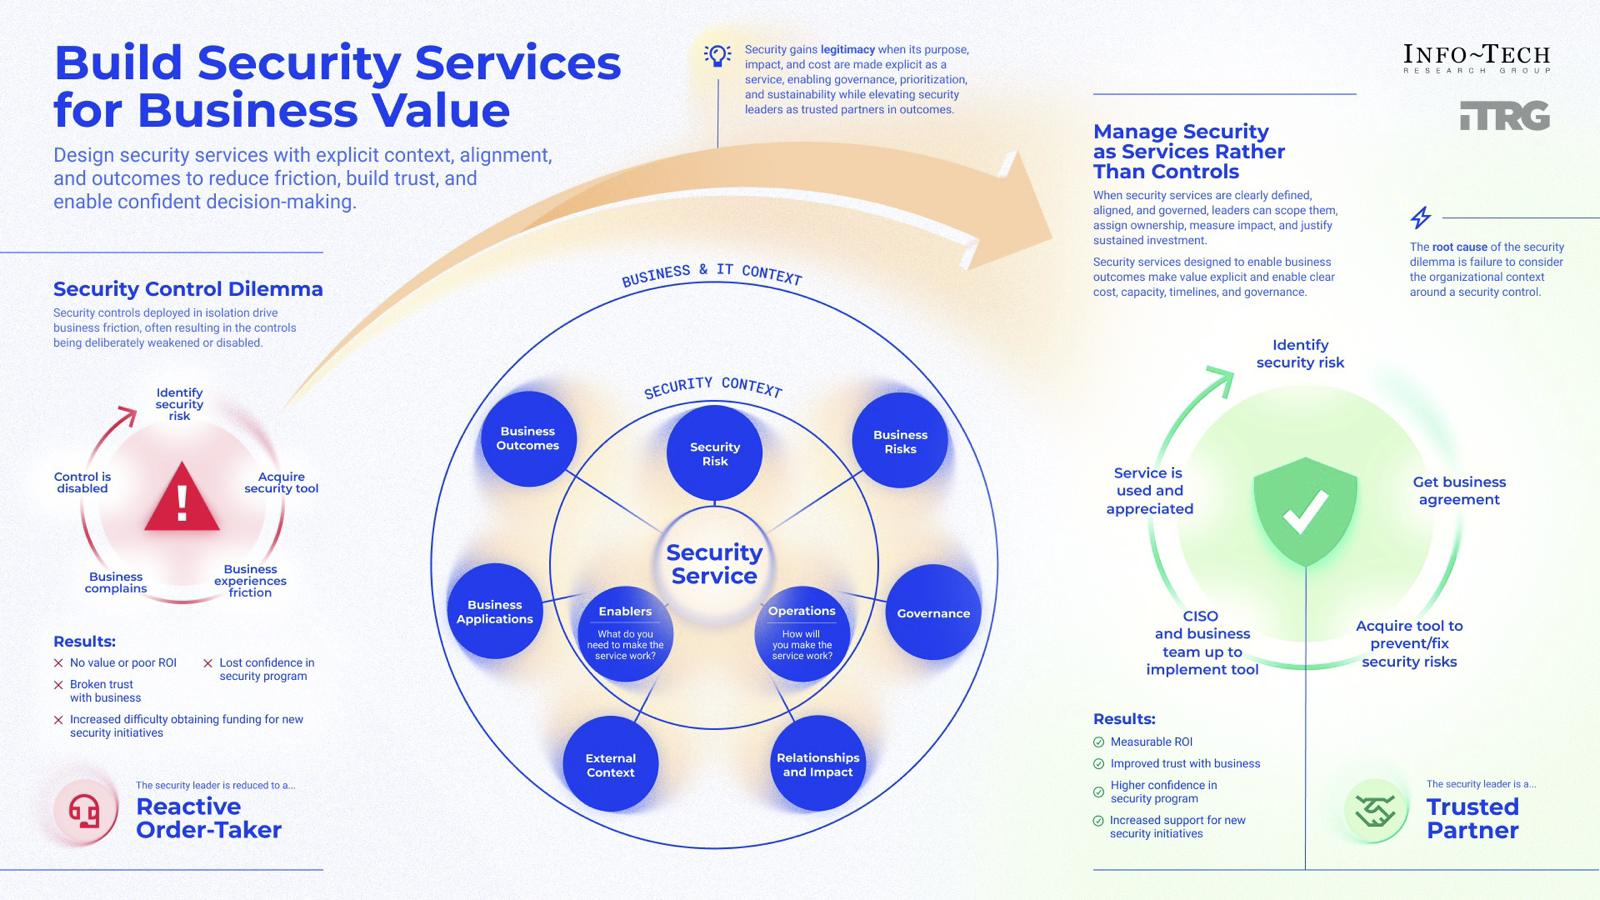
Security gains legitimacy when it ceases to be an isolated control and instead functions as a supportive business enabler.
Security Service Design
- Understand security service context
- Align with business priorities
- Plan, communicate, and market
- Sustain and evolve
The Info-Tech difference:
This research helps you design security services as built‑in enablers instead of bolted‑on barriers.
- Ground every security service in a clear understanding of why it exists, who it enables, and how it supports business outcomes.
- Design around shared business outcomes to make security services the drivers of performance and resilience, not constraints that slow execution.
- Market security services using narratives leaders understand: value delivered, risk reduced, and outcomes achieved. When the story resonates, services get prioritized, funded, and used as intended.
Info-Tech’s methodology for building security services for business value
Phase Steps |
1. Map Your Security Service Context
|
2. Align Your Security Service to a Business Service
|
3. Analyze, Finalize, and Communicate
|
Phase Outcomes |
A clearly defined security service grounded in business context, with shared understanding of who it supports, how it creates value, and the internal and external factors that shape its design. This ensures security is framed as part of the business reality, not an isolated technical function. | An integrated security service design aligned to customer and business outcomes, with controls embedded into business services. Security, technology, governance, and risk are aligned around a shared vision of success. | A practical, resourced plan to operationalize and sustain the security service, supported by clear ownership, funding logic, and success metrics. Security is positioned as a durable, business‑enabling service that can be adopted, measured, and continuously improved. |
AInsight Summary
Stop releasing controls the business avoids. Use Info‑Tech’s service‑centric method to build security services that your business partners trust, prioritize, and fund.
Overarching Insight
Security gains legitimacy when its purpose, impact, and cost are made explicit as a service. This enables security leaders to move from enforcing controls to enabling business outcomes as trusted partners.
Understand your service’s value and purpose
When security decisions are grounded in shared context, leaders can clearly see what they are being asked to support, why it matters, and what trade‑offs are involved.
Support business outcomes with your design
Security services are much more than isolated controls; they are supporting services embedded within business services to enable business outcomes. Integrated security services that facilitate business outcomes remain usable, beneficial, and willingly adopted, while isolated security controls that impede business operations are avoided, underfunded, or removed.
Promote and champion your service’s benefits and needs
Business leaders support what they understand. Communicate and market clear work, risks, needs, and costs so they can confidently prioritize and fund your security service.
Blueprint deliverables
Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:
Security Service Communication Template
Use this template to create an audience-ready document to communicate and market your security service.
Security Service Roadmap Tool
Use this tool to create a visual roadmap that supports your security service in becoming a reality.
Key deliverable:
Security Service Workbook
This workbook helps you describe your service in its business context, align it to an impacted business service, and estimate costs.
About Info-Tech
Info-Tech Research Group is the world’s fastest-growing information technology research and advisory company, proudly serving over 30,000 IT professionals.
We produce unbiased and highly relevant research to help CIOs and IT leaders make strategic, timely, and well-informed decisions. We partner closely with IT teams to provide everything they need, from actionable tools to analyst guidance, ensuring they deliver measurable results for their organizations.
What Is a Blueprint?
A blueprint is designed to be a roadmap, containing a methodology and the tools and templates you need to solve your IT problems.
Each blueprint can be accompanied by a Guided Implementation that provides you access to our world-class analysts to help you get through the project.
You Get:
- Build Security Services for Business Value Deck
- Security Service Workbook
- Security Service Communication Template
Talk to an Analyst
Our analyst calls are focused on helping our members use the research we produce, and our experts will guide you to successful project completion.
Book an Analyst Call on This Topic
You can start as early as tomorrow morning. Our analysts will explain the process during your first call.
Get Advice From a Subject Matter Expert
Each call will focus on explaining the material and helping you to plan your project, interpret and analyze the results of each project step, and set the direction for your next project step.
Unlock Sample ResearchContributors
- Greg Atkinson, Senior Manager, Cyber Security Systems, McMaster University
- Tracy Dallaire, Deputy Chief Technology Officer and Director, Digital Experience, McMaster University
- Doug Jaworski, CISO
 Design and Implement a Business-Aligned Security Program
 Build a Security Strategy
 Secure Operations in High-Risk Jurisdictions
 Develop a Security Awareness and Training Program That Empowers End Users
 Build, Optimize, and Present a Risk-Based Security Budget
 Hire or Develop a World-Class CISO
 Fast Track Your GDPR Compliance Efforts
 Build a Cloud Security Strategy
 Identify the Components of Your Cloud Security Architecture
 Security Priorities 2022
 2020 Security Priorities Report
 Manage Third-Party Service Security Outsourcing
 Select a Security Outsourcing Partner
 Improve Security Governance With a Security Steering Committee
 The First 100 Days as CISO
 Determine Your Zero Trust Readiness
 Cost-Optimize Your Security Budget
 Threat Preparedness Using MITRE ATT&CK®
 Build a Zero Trust Roadmap
 Security Priorities 2023
 Security Priorities 2024
 Grow Your Own Cybersecurity Team
 Security Priorities 2025
 Create a Zero Trust Implementation Plan
 Run IT By the Numbers
 Transform IT, Transform Everything
 The Race to Develop Talent
 Assessing the AI Ecosystem
 Bring AI Out of the Shadows
 IT Spend and Staffing Benchmarking
 The Security Playbook
 Security Priorities 2026
 Build Security Services for Business Value
