
Build a Data Privacy Program
Take out data privacy’s grey areas with a quantitative approach to your program.
- Data privacy has become a baseline business expectation, regardless of company size or industry.
- With a multitude of regulatory frameworks to consider, business and IT leaders find themselves scrambling to ensure that all bases are covered when it comes to data privacy.
Our Advice
Critical Insight
- Take a quantitative approach to data privacy.
- Use metrics and a risk-based approach to drive a privacy framework that not only supports compliance but also considers the custom needs of your organization.
Impact and Result
- Sell privacy to the business by speaking a language they understand. IT and InfoSec leaders need to see privacy as not just compliance but also a driver of business efficiency.
- Integrate and build by developing a program that:
- Promotes freedom of information and access to this information.
- Establishes privacy and security standards with respect to access of this information.

On Demand
Webinar

Reduce Risks With a Quantitative Approach to Privacy Compliance
Play WebinarMember Testimonials
After each Info-Tech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve. See our top member experiences for this blueprint and what our clients have to say.
8.4/10
Overall Impact
$71,412
Average $ Saved
43
Average Days Saved
Client
Experience
Impact
$ Saved
Days Saved
County of Los Angeles, CA - Department of Public Works
Guided Implementation
10/10
$134K
10
Government of Bermuda
Workshop
8/10
$68,999
10
Best - to see that we have actually made progress Worst - the feeling that we still are trying to get answers on some of the same questions
Member Organization
Guided Implementation
9/10
$13,600
32
Best: we learned a lot of what we did not know about data privacy. Worst: the material seemed more complex than what we need. I'm wondering if t... Read More
Member Organization
Guided Implementation
5/10
N/A
N/A
Probably not fair to rate this, as we have pivoted internally.
Member Organization
Guided Implementation
10/10
$68,500
120
Member Organization
Guided Implementation
10/10
$5,199
5
As usual Alan helped align my direction. His advice is very much appreciated.
Member Organization
Guided Implementation
10/10
$47,500
50
Best is the use of the existing blueprints that I can re-use and support received
Member Organization
Workshop
10/10
$649K
60
Partner with other software solutions to have a repository of where to store the information gathered that is more dynamic than using spreadsheets ... Read More
Member Organization
Workshop
10/10
$97,499
60
This was my first experience attending a workshop faciliated by InfoTech. I really enjoyed the workshop. I thought the faciliator (Alan Tang) did a... Read More
Member Organization
Guided Implementation
10/10
$6,499
2
Member Organization
Guided Implementation
10/10
$2,469
5
Member Organization
Guided Implementation
10/10
$31,499
20
Iris is knowledgeable, friendly and experienced. I am pleased to have had the opportunity to connect with her and consider her an ally on all thing... Read More
Member Organization
Guided Implementation
10/10
$62,999
50
Feeling assured that Alan and InfoTech have the expertise to review our drafts and provide constructive feedback as and when needed that we can act... Read More
Member Organization
Workshop
10/10
$37,799
120
I'm not sure how you put a monetary value on this. I believe that while you can value staff time, it is hard to put a value on the effects of deve... Read More
Member Organization
Guided Implementation
10/10
$37,799
14
Alan really knows the Privacy law arena and is invaluable in the guidance that he gives. I leave each session feeling like I have a good handle on ... Read More
Member Organization
Workshop
10/10
N/A
50
The workshops get the work done much faster and gets everybody on board with what needs to be done.
Member Organization
Guided Implementation
9/10
$62,999
50
Post workshop having Alan available to call and offer guidance and expertise has been great, he is a guide and a sounding board, offering practical... Read More
Member Organization
Guided Implementation
9/10
$62,999
20
Alan is great, he provides guidance that I can actually apply. I look forward to engaging further with Alan.
Member Organization
Guided Implementation
8/10
N/A
N/A
Incredibly valuable guidance on our Privacy Operations roadmap! Still too early to estimate the time and financial impact but we anticipate it will... Read More
Member Organization
Guided Implementation
9/10
$31,499
10
Member Organization
Guided Implementation
9/10
N/A
N/A
Alan, was very knowledgeable and provided good insight. His follow through was outstanding. At this point, it is difficult to determine how much ... Read More
Member Organization
Workshop
8/10
$1.17M
20
Best - getting so much done in only a few days while still allowing everyone to express concerns, opinions, advice, and even frustrations. Worst... Read More
Member Organization
Guided Implementation
10/10
$29,609
20
Alan is awesome - he helped to establish our roadmap that gives us a trajectory to succeed. I truly appreciate Alan's help!
Member Organization
Guided Implementation
10/10
$31,499
N/A
While still new on approach and hard to estimate, I can see value already.
Member Organization
Guided Implementation
10/10
$2,519
5
Understood our challenges and was able to provide actionable data to back future discussions.
Member Organization
Guided Implementation
10/10
$2,393
5
Member Organization
Workshop
9/10
N/A
14
Best: Opportunity to have conversations with our Exec team and key staff on privacy related topics with the expertise of Alan Tang delivering key ... Read More
Member Organization
Guided Implementation
9/10
$12,599
2
Member Organization
Workshop
10/10
$37,400
100
The best part of the workshop is the roadmap to a data privacy program. In addition, although the resources are available for a self-guided impleme... Read More
Member Organization
Guided Implementation
8/10
N/A
N/A
Best - learning that such a credentialed expert was part of the Info-Tech team and accessible to us for guidance. Also best - Actual guidance! ... Read More

Privacy Program Management
Participants will gain a comprehensive understanding of privacy management, including how to collect privacy requirements, conduct a privacy gap analysis, build a privacy roadmap, and implement and operationalize privacy practices.
- Course Modules: 5
- Estimated Completion Time: 8 hours
Workshop: Build a Data Privacy Program
Workshops offer an easy way to accelerate your project. If you are unable to do the project yourself, and a Guided Implementation isn't enough, we offer low-cost delivery of our project workshops. We take you through every phase of your project and ensure that you have a roadmap in place to complete your project successfully.
Module 1: Collect privacy requirements
The Purpose
- Understand the key drivers behind privacy in your operating context and begin to assign ownership.
Key Benefits Achieved
- Level-setting between IT and the business with respect to privacy best practices.
- High-level understanding of risk associated with personal data collected by the organization.
Activities
Outputs
Define and document program drivers.
Establish privacy governance structure and define scope.
Build the Privacy RACI.
Build the risk map.
- Business context and drivers behind privacy program
- Privacy RACI chart
Module 2: Conduct a privacy gap analysis
The Purpose
- Connect with each of the business units with respect to current privacy practices and gain insight into how personal data is handled throughout the organization.
Key Benefits Achieved
- Alignment with business unit privacy champions
- Understanding of current state of privacy in the organization
- Uncovered gaps in the organization’s privacy practices
Activities
Outputs
Conduct interviews and complete Data Process Mapping tool.
Compare compliance and regulatory requirements with current privacy practices of the organization.
Identify gap areas.
Review the DPIA process and identify whether threshold assessment or full DPIA is required.
- Data Process Mapping tool draft
- Mapped privacy control gap areas to relevant privacy laws, frameworks, or industry standards
- Optional: Walkthrough of DPIA tool
Module 3: Build the privacy roadmap
The Purpose
- Ensure that the privacy program is functional and caters to the environment assessed over days 1 and 2 by building a custom-fit privacy initiative implementation roadmap.
Key Benefits Achieved
- Quantitative prioritization of each of the privacy gap closing initiatives
- High-level initiative implementation roadmap
Activities
Outputs
Complete business unit gap analysis; consolidate inputs from Day 2 interviews.
Apply variables to privacy initiatives.
Create a visual privacy roadmap.
Define and refine the effort map; validate costing and resourcing.
- Privacy Framework Tool
- Privacy Roadmap and prioritized set of initiatives
Module 4: Implement and operationalize
The Purpose
This portion of the workshop ensures that the privacy program can be put into action and moves beyond static policies to foster the integration of privacy metrics across the organization.
Key Benefits Achieved
A full set of privacy metrics, as well as tactics to implement and monitor on an ongoing basis.
Activities
Outputs
Review Info-Tech’s privacy metrics and select relevant metrics for the privacy program.
Operationalize metrics.
Input all outputs from days 1-3 into the Data Privacy Report.
Summarize and build an executive presentation.
Set checkpoints and drive continuous improvement.
- Completed Privacy Roadmap
- Completed Data Process Mapping tool
- Review of any outstanding privacy collateral (Privacy Notice, Data Protection Policy, etc.)
- Privacy Program Report document
Build a Data Privacy Program
Take out data privacy's grey areas with a quantitative approach to your program.
Analyst Perspective
Privacy can no longer be subjective. Quantify and measure to drive a more effective privacy program.
With an explosion of data breaches highlighted almost daily across the globe, and an ever-expanding web of heavy-handed privacy laws and regulatory frameworks, privacy demands sustained attention from both IT and the business.
This leaves leaders questioning how to best approach privacy and operationalize it at scale for their respective organization. As a facet of the business that has traditionally been left to the discretion of a legal team or professional(s), execution of privacy and data protection remains a shrouded, grey area for many organizations.
But what if privacy is a little more "black and white" than what previous thought frameworks may have dictated? By taking a quantitative vs. qualitative approach to privacy management, business and IT leaders can remove some of the ambiguity around what privacy controls need to be in place and how to balance privacy integration with current business operations.
As the general public continues to take back control over data privacy, so too should organizations by taking a tactical, measurable approach to privacy and the business.
Seva Ioussoufovitch
Senior Research Analyst,
Security & Privacy,
Infotech
Executive Summary
Your Challenge
- Data privacy has become a baseline business expectation, regardless of company size or industry.
- With a multitude of regulatory frameworks to consider, business and IT leaders find themselves scrambling to ensure that all bases are covered when it comes to data privacy.
- Privacy teams are having a difficult time conveying their legal obligations and providing actionable guidance to business partners.
Common Obstacles
- Privacy, traditionally, has existed in a separate realm, resulting in an unintentional and problematic barrier drawn between the privacy team and the rest of the organization.
- With many regulatory frameworks to consider and a number of boxes to tick off, building an all-encompassing data privacy program becomes increasingly challenging.
Infotech's Approach
- Sell privacy to the business by speaking a language they understand. Privacy and IT leaders need to see privacy not just as compliance, but as a driver of business efficiency.
- Integrate and build by developing a program that promotes:
- Privacy standards that are established with respect to how information is accessed.
- Accessibility to this information through a defined understanding of personal data's processing standards in the organization.
Infotech Insight
Take a quantitative approach to data privacy. Use metrics and a risk-based approach that supports compliance while considering the custom needs of your organization.
Your challenge
This research is designed to help organizations who need to:
- Understand how to adapt and quantify privacy beyond compliance.
- Change the pre-existing perspective on how to assess privacy competency.
- Shift the organization's view of privacy as the enemy of efficiency and innovation.
- Build an environment that places privacy ownership in the hands of the business.
- Extend the privacy program beyond the privacy team or organizational function.
- Take the ambiguity out of privacy program management.
Understand > Assess > Bridge > Implement
Data Privacy Program
1. Collect Privacy Requirements
2. Conduct a Privacy Gap Analysis
3. Build the Privacy Roadmap
4. Implement and Operationalize
Privacy is all about personal data
When building a privacy program, focus on all personal data, whether it's publicly available or private. This includes defining how the data is processed, creating notices and capturing consent, and protecting the data itself. On the converse side, an effective privacy program also enables accessibility to information based on regulatory guidance and appropriate measures.
Examples of Personal Data
Traditional PII
Personally Identifiable Information
Full name (if not common)
Home address
Date of birth
Social security number
Banking information
Passport number
Etc.
Personal Data
Any information relating to an identified or identifiable person
First, middle (if applicable), last name
IP address
Email address or other online identifier
Social media post
Location data
Photograph
Etc.
Sensitive Personal Data
Special categories of personal data (some regulations, like GDPR, expand their scope to include these)
Biometrics data: Retina scans, voice signatures, or facial geometry
Health information: Patient identification number or health records
Political opinions
Trade union membership
Sexual orientation and/or gender identity
Religious or philosophical beliefs
Ethnic origin
Understanding privacy vs. security
A common assumption is that security and privacy are one and the same. Security's role is to protect and secure assets, of which confidential data – especially personal data – is a large focus. The consequences of a personal data breach can be severe, including the loss of customer trust and potential regulatory consequences. As a result, we often think of how we use security to protect data.
But that is not equivalent to privacy …
Privacy must be thought of as a separate function. While there will always be ties to security in the ways it protects data, privacy starts and ends with the focus on personal data. Beyond protection, privacy extends to understanding why personal data is being collected, what the lawful uses are, how long it can be retained, and who has access to it.
True cost of a data breach
An industry outlook
Even with a robust privacy program in place, organizations are still susceptible to a data breach. The benefit comes from reducing your risk of regulatory compliance and resulting fines and minimizing overall exposure.
67% of data breach costs are associated with regulatory fines.
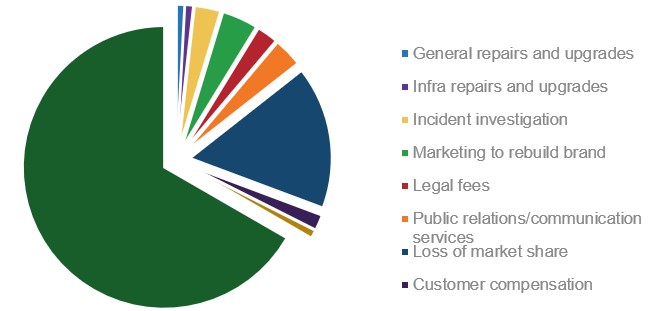
Healthcare1
Estimated Cost of Exposure:
$574.75 k
Government
Estimated Cost of Exposure:
$467.5 k
Financial Services
Estimated Cost of Exposure:
$522.5 k
Education
Estimated Cost of Exposure:
$375 k
1 All fine estimates are based on an annual turnover of US$10 million and 1,000 lost records
Source: Proteus-Cyber
2025 Breach Breakdown
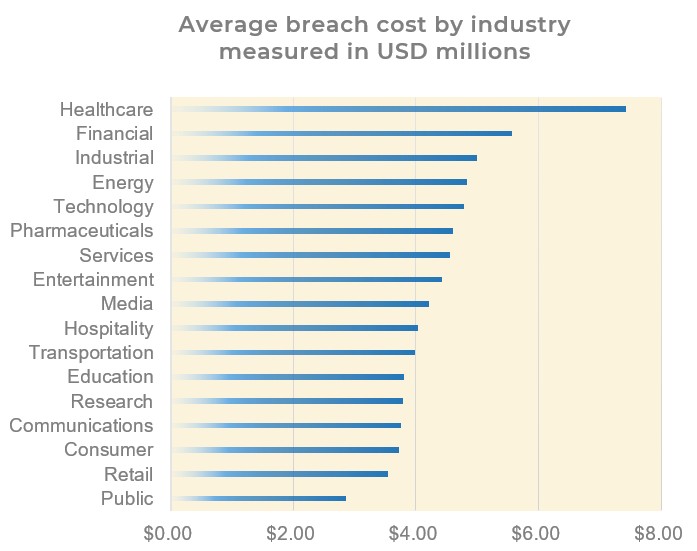
The global average data breach cost was $4.44 million USD in 2025.
Source: IBM, 2025.
The Data Breach Aftermath
A third of organizations paid a regulatory fine due to a data breach.
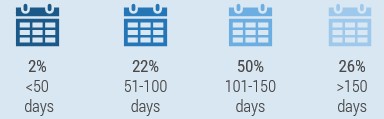
Data breach resolution times
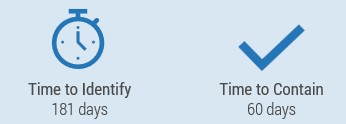
% of data breach recovery time
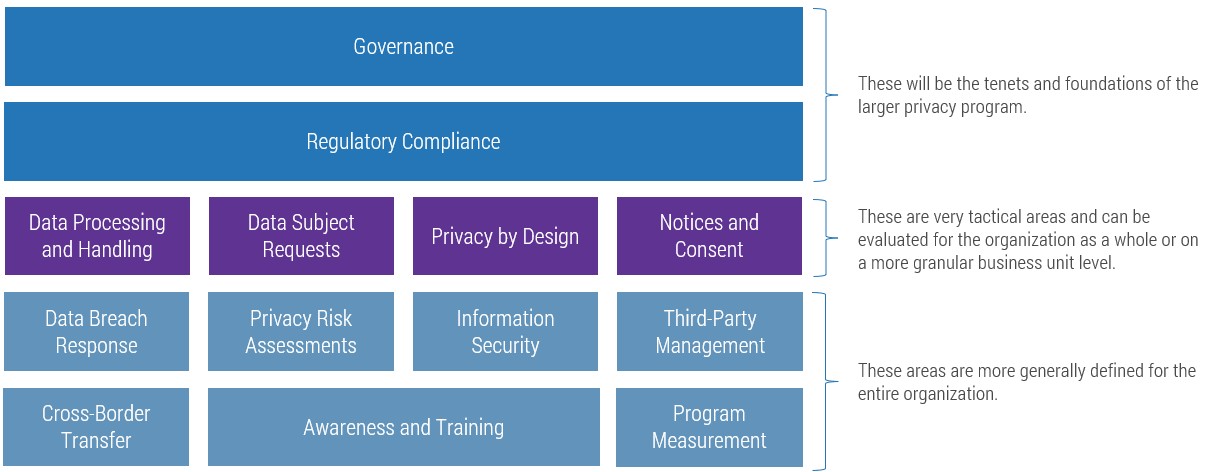
Infotech's Privacy Program Methodology
The below image is a visual representation of Infotech's Privacy Framework. This includes high-level governance items as well as more tactically defined areas. See an overview below.
Data privacy law intersects with AI
Existing automated decision-making obligations extend to AI systems.
- The General Data Protection Regulation (GDPR) took effect in May 2018 and became somewhat of a global standard for data protection.
- While the GDPR preceded the current wave of generative AI, it included provisions around automated decision-making. These provisions are an important foundation for governing decisions made without human involvement, and some AI-driven decisions are naturally included within them.
- Broader governance of automated decision-making is becoming a key consideration in other pieces of regulation.
- For example, 2025 saw regulations finalized under the CCPA that specifically address automated decision-making technology.
The EU AI Act is another key piece of AI legislation. While it isn't a privacy law, AI tools labeled high-risk under this legislation (e.g. hiring tools) are subject to additional logging and transparency requirements.
Privacy controls focused on automated decision-making can manage some of the novel risks introduced by AI. A bigger challenge is that many organizations still build and deploy AI projects in silos, without looping back to the privacy program at all.
Infotech Insight
AI projects should at least be routed through the same privacy assessments as other data processing activities. That said, evolving PIAs to account for AI-specific risks will strengthen your privacy program's ability to keep pace.
Related AI Privacy Risk Research
AI extends the privacy control framework
The risks introduced by AI don't require you to rebuild your privacy program, but they may require you to extend its control capabilities. While control applicability depends on which regulations your organization must comply with, more jurisdictions are starting to adopt provisions that would require similar controls.
Privacy regulatory compliance must consider AI-specific risks and obligations. This is addressed by creating a distinct AI system inventory and assessing systems that deal with personal data against any applicable privacy regulations with AI-specific obligations.
The right to challenge automated decisions extends to those made by AI systems. Data subjects must be able to express their view, request human review, and contest any decision based on or significantly informed by automated processing.
AI agents or agentic AI systems make autonomous decisions based on personal data. As such, Privacy by Design now also includes documenting business, technical, and privacy requirements before agent deployment.
Notices and Consent must also specifically cover automated decisions. Data subjects should be informed of automated decisions, including the logic, significance, and consequences involved, with appropriate or necessary consent obtained.
Infotech Insight
AI does not change the fundamental mandate and focus of privacy: to protect personal data. However, it adds new mechanisms that act and make decisions based on that data which your program must be ready to account for.
AI pushes data privacy beyond compliance
The emergence of AI has pushed privacy programs to move beyond their traditional focus on regulatory compliance and act as an enabler for building trust between organizations and their customers.
90% of organizations report AI has expanded the scope of their privacy programs.
Nearly half of organizations indicate that transparency about data collection and use is the top action to build customer trust.
Source: Cisco, 2026.
Just 55% of organizations require AI vendors to provide contractual terms of data ownership, responsibility, and liability.
Infotech Insight
An effective privacy program ensures compliance, but simply being compliant does not mean you have an effective privacy program.
Instead of reactively checking off the data privacy compliance boxes based on a set of governing laws, develop a privacy framework that proactively anticipates new pressures, like those introduced by AI, while staying in scope of the needs of your organization.
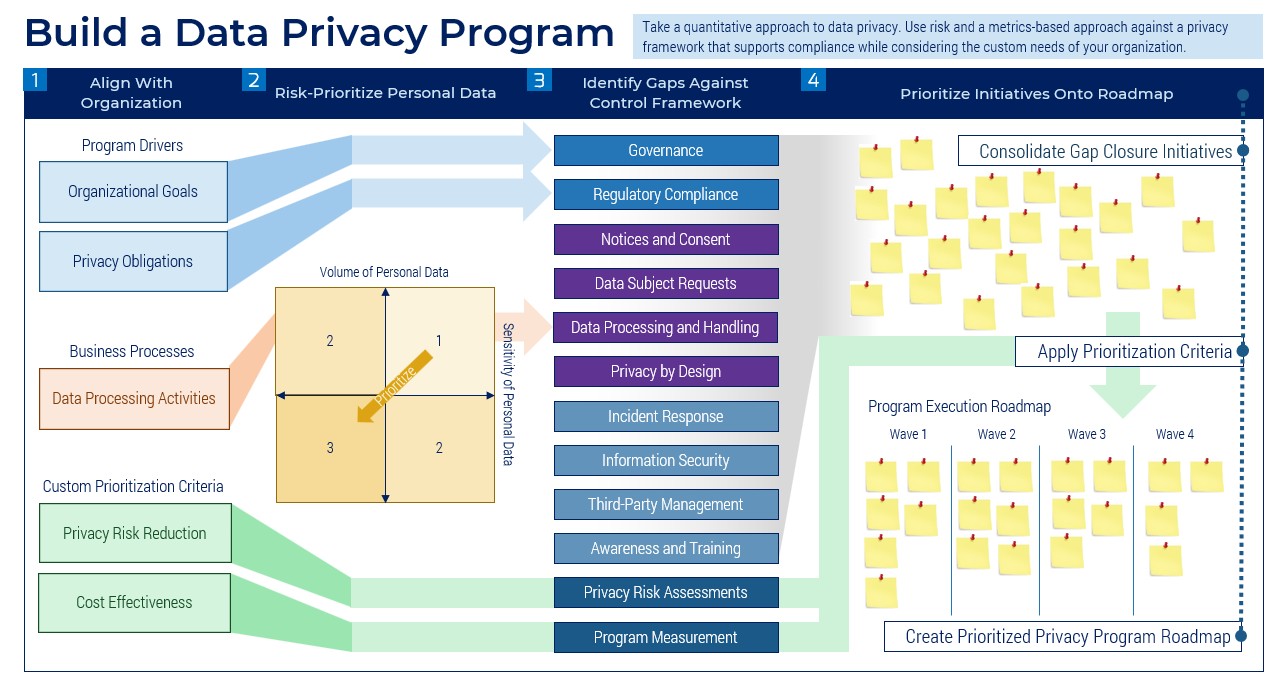
Infotech's methodology for building a privacy program
| 1. Collect Privacy Requirements | 2. Conduct a Privacy Gap Analysis | 3. Build the Privacy Roadmap | 4. Implement and Operationalize | |
|---|---|---|---|---|
| Phase Action Items |
|
|
|
|
| Phase Outcomes |
|
|
|
|
Insight summary
Fit privacy to the business.
Contextualize privacy for your organization by involving the business units from day 1; collect requirements that promote cross-collaboration.
Privacy is dynamic.
Structure drives success: take a process vs. system-based approach to assessing personal data as it flows throughout the organization.
Prioritize and plan together.
Review, revise, reprioritize; come back to the initial risk map created. Draw on areas of alignment between high-value/high-risk processes and their supporting initiatives to properly prioritize.
Privacy doesn't live in isolation.
By assigning ownership and flexibility to your business units in how they weave privacy into their day-to-day, privacy becomes part of operational design and structure.
A good privacy program takes time.
Leverage the iterative process embedded in each phase to prioritize privacy initiatives based on value and risk and support the rollout through customized metrics.
Make it operational.
Be selective with your metrics: choose to implement only metrics that are relevant to your environment. Base your selection on the highlighted areas of focus from the maturity assessment.
Take a quantitative approach to data privacy.
Use metrics and a risk-based approach to drive a privacy framework that supports compliance and considers the custom needs of your organization.
Blueprint deliverables
Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals:
Privacy Program RACI Chart
A high-level list of privacy program initiatives, with assigned ownership to privacy champions from both the business and IT.
Data Process Mapping Tool
Full documentation of all business processes that leverage personal data within the organization.
Data Protection Impact Assessment
When highly sensitive data is involved, leverage this tool to assess whether appropriate mitigating measures are in place.
Data Privacy Program Report
A template that summarizes all key findings of the blueprint.
Privacy Policy Templates
Internal and external policies:
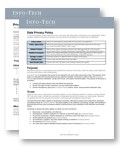
- Data Privacy Policy
- Privacy Notice
- Cookie Policy
Key deliverable:
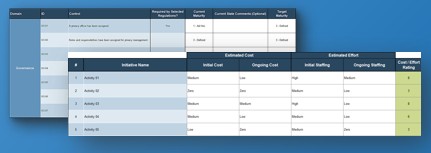
Privacy Framework Tool
Leverage best-practice privacy tactics to assess your current organizational privacy maturity while comparing against current privacy frameworks, including GDPR, CCPA, HIPAA, and NIST.
Build your gap-closing initiative roadmap and work through cost/effort analysis.
Blueprint benefits
| IT Benefits | Business Benefits |
|---|---|
|
|
Infotech Insight
Turn strong privacy and data protection capabilities into your competitive advantages. Being privacy compliant can improve customer retention and loyalty.
Measure the value of this blueprint
As better privacy becomes the expectation from both B2B customers and end-consumers, expect a subsequent shift toward a strong privacy program as a competitive advantage for many organizations.
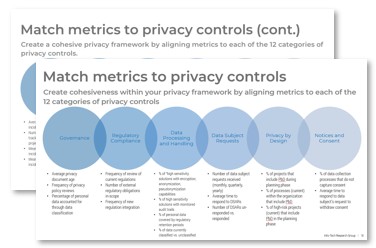
Privacy metrics take your program from a static framework to an operational model.
Select privacy metrics that are realistic and relevant for your organization, based on each of the 13 areas outlined as part of privacy control best practices.
Infotech's Privacy Control Categories
- Governance
- Regulatory Compliance
- Data Processing and Handling
- Data Subject Requests
- Privacy by Design
- Notices and Consent
- Data Breach Response
- Privacy Risk Assessments
- Information Security
- Third-Party Management
- Cross-Border Transfer
- Awareness and Training
- Program Measurement
After each Infotech experience, we ask our members to quantify the real-time savings, monetary impact, and project improvements our research helped them achieve.
Overall Impact
8.4 / 10
Overall Average Savings
$38,824
Overall Average Days Saved
42
Executives are increasingly concerned about data breaches
Hefty fines and reputational damage are two of the primary setbacks incurred following a publicized data breach.
$4.44 million
Average total cost of a data breach (USD)
2,960–113,620
Records exposed per breach
241 days
Time between occurrence and containment of data breach
Phishing
Top breach type for number of incidents incurred
Senior management and executives now acknowledge privacy and security as some of the biggest risks to the business. Previously, the entire scope of privacy would fall upon IT professionals to manage and control.
High-profile cyberattacks and data breaches have brought the issue of privacy to the forefront of executives' minds. Regulatory obligations to notify the public of breaches and pay significant fines for noncompliance have also pushed executives to be more concerned than ever before.
Infotech Insight
Data breaches shouldn't just concern senior leadership and management; involving and educating your organization at all levels encourages a tightly woven, privacy-centric operating model.
Source: IBM, 2025.
Executive brief case study
Allianz Life Data Breach – July 2025
INDUSTRY
Insurance
SOURCES
Forbes, Proven Data, Claim Depot
Event
- Allianz Life, a major insurance company, announced a data breach in July 2025 that impacted nearly 1.4 million of its customers.
- PII hacked included names, addresses, birth dates, Social Security Numbers, contact details, and insurance policy information.
Aftermath
- Allianz provided affected customers with a complimentary 24-month identity theft protection and credit monitoring package.
- A class action lawsuit was filed against Allianz Life that alleged the company failed to meet industry security standards.
- The company stated they would focus on implementing:
- Stricter controls for payment processing and customer account changes.
- Stronger transaction authentication and analysis.
Issue
- Employees fell victim to social engineering: threat actors impersonated IT help desk and tricked Allianz staff into providing access to the company's Salesforce CRM.
- Inadequate third-party vendor access controls: compromised credentials gave attackers unrestricted access to the CRM, where they used a built-in tool to bulk export records. Stronger enforcement of least-privilege access and anomaly detection could have reduced the impact of the breach.
Infotech's Resolution
Preventing a data breach is just one outcome of implementing an effective privacy program, among an understanding of:
- Where every bit of personal information resides
- Who has access to which personal information
- All security controls necessary to protect personal information
- The retention times for different types of PII
Build a Data Privacy Program leverages a simple four-step process:
- Collect Privacy Requirements
- Conduct a Gap Analysis
- Build the Privacy Roadmap
- Implement and Operationalize
On Demand
Webinar
Reduce Risks With a Quantitative Approach to Privacy Compliance
Play Webinar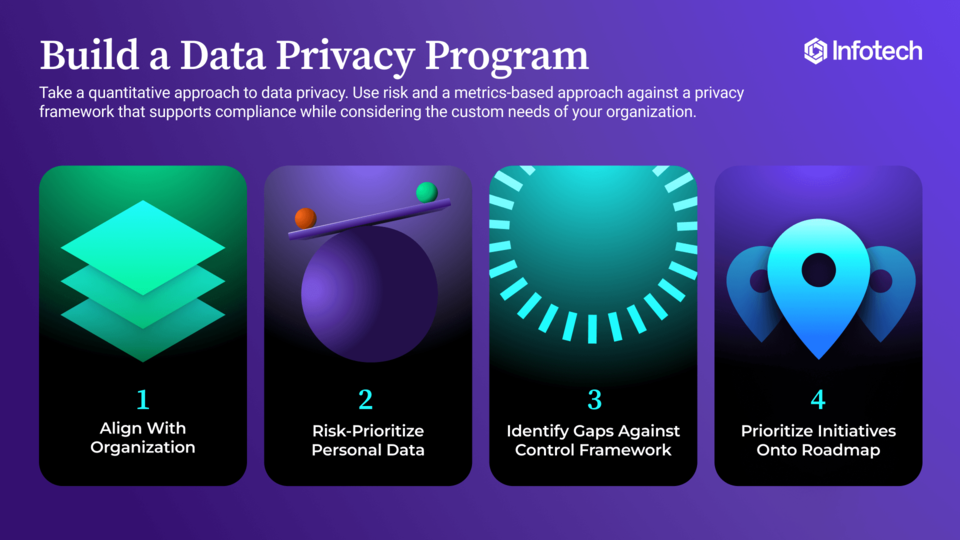
About Info-Tech
Info-Tech Research Group is the world’s fastest-growing information technology research and advisory company, proudly serving over 30,000 IT professionals.
We produce unbiased and highly relevant research to help CIOs and IT leaders make strategic, timely, and well-informed decisions. We partner closely with IT teams to provide everything they need, from actionable tools to analyst guidance, ensuring they deliver measurable results for their organizations.
What Is a Blueprint?
A blueprint is designed to be a roadmap, containing a methodology and the tools and templates you need to solve your IT problems.
Each blueprint can be accompanied by a Guided Implementation that provides you access to our world-class analysts to help you get through the project.
Need Extra Help?
Speak With An Analyst
Get the help you need in this 4-phase advisory process. You'll receive multiple touchpoints with our researchers, all included in your membership.
Guided Implementation 1: Collect privacy requirements
- Call 1: Scope requirements, drivers, objectives, and challenges.
- Call 2: Build out privacy ownership using the RACI chart.
Guided Implementation 2: Conduct a privacy gap analysis
- Call 1: Review results of data process mapping business unit interviews.
- Call 2: Delve into the Privacy Framework Tool to identify and evaluate gaps.
Guided Implementation 3: Build the privacy roadmap
- Call 1: Determine cost and effort ratio of gap initiatives.
- Call 2: Build out additional privacy collateral (notice, policy, etc.).
Guided Implementation 4: Implement and operationalize
- Call 1: Review standard privacy metrics and customize for your organization.
- Call 2: Establish and document performance monitoring schedule.
Contributors
- Alan Tang, Security Professional
- Salvador Barragan, Director of Records & Information Governance, Pekin Insurance
 Privacy by Design for Digital Marketing
 Build a Data Privacy Program
 Mature Your Privacy Operations
 Fast Track Your GDPR Compliance Efforts
 Secure Your High-Risk Data
 Ensure Your Pandemic Response Plan Is Privacy-Proof
 Comply With the California Consumer Privacy Act
 Build an Effective Data Retention Program
 Demonstrate Data Protection by Design for IT Systems
 Tech Trend Update: If Digital Ethics Then Data Equity
 Conduct an AI Privacy Risk Assessment
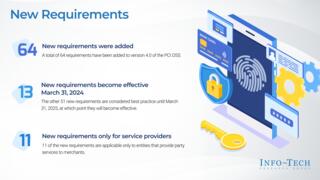 Prepare for PCI DSS v4.0
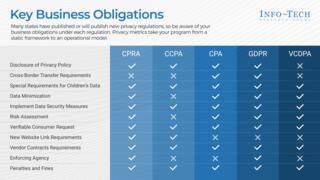 Comply With the California Privacy Rights Act
 Comply With 2023 US Privacy Laws (Virginia, Connecticut, Utah, Colorado)
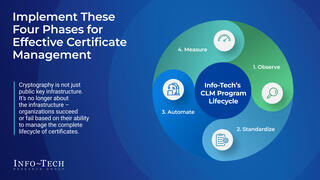 Master Certificate Lifecycle Management
