
Assess and Prioritize Agentic AI Use Cases in Pharmaceutical Manufacturing
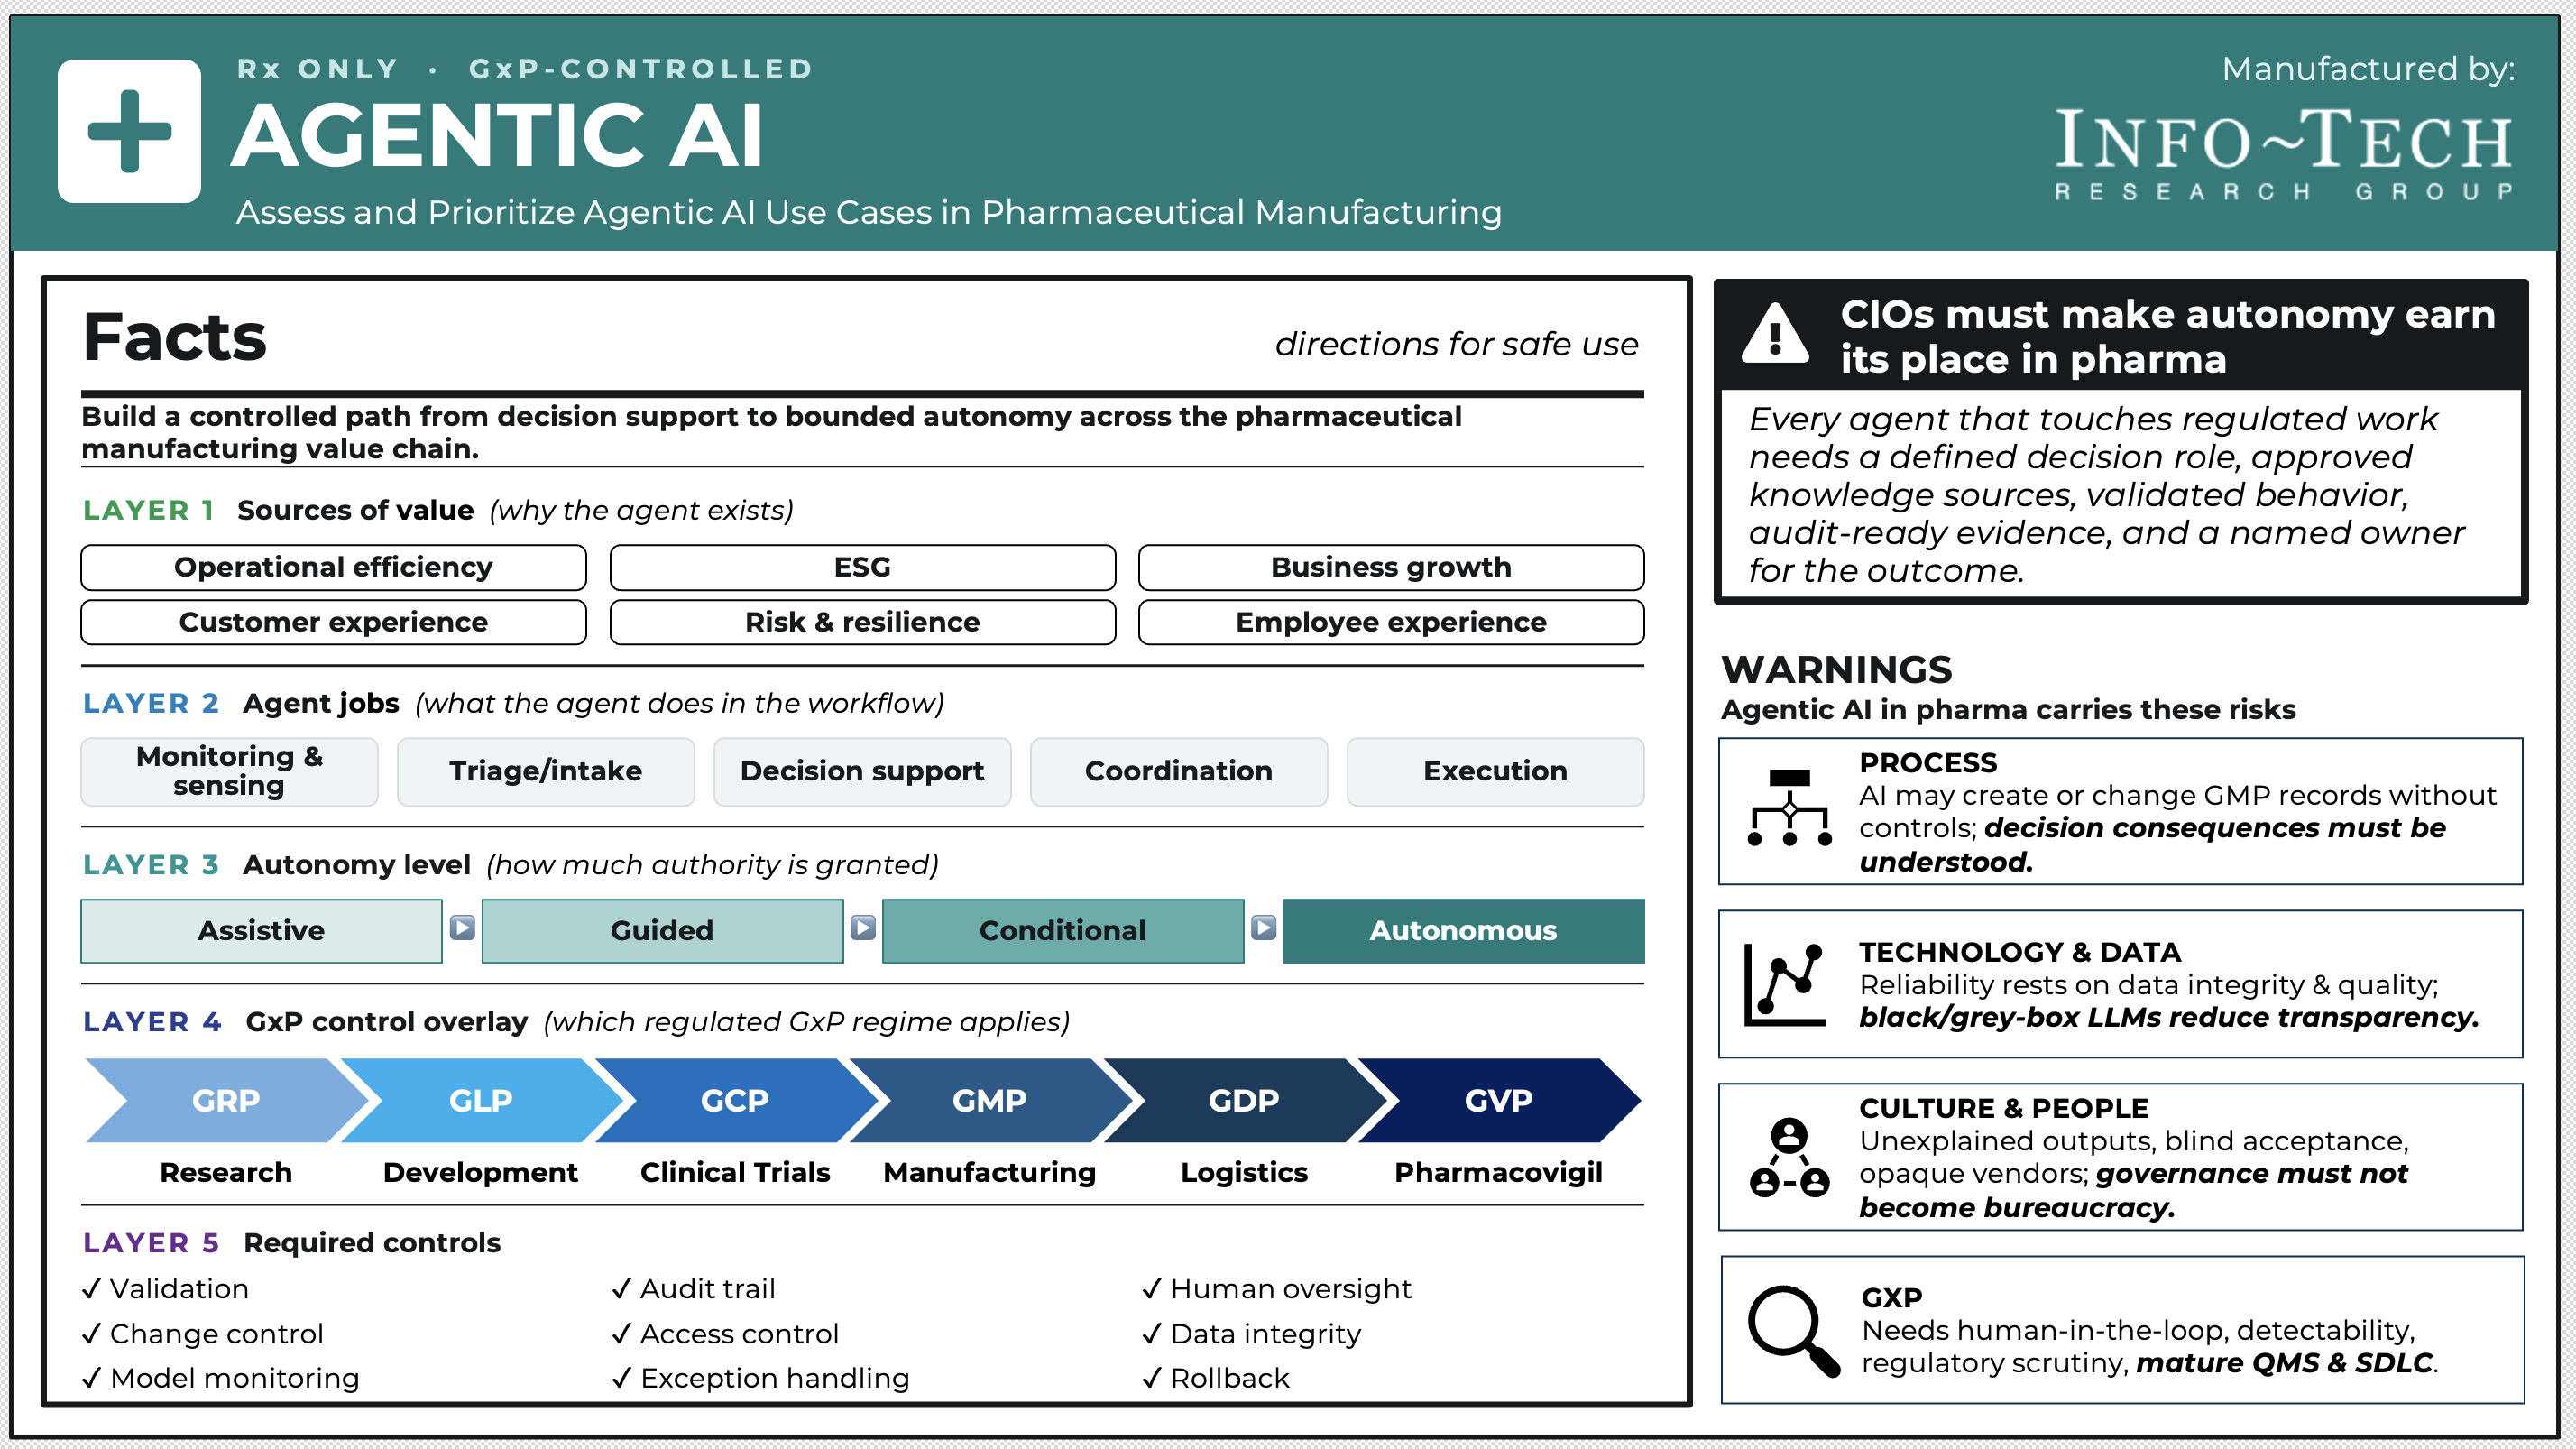
Build a controlled path from decision support to bounded autonomy across the pharmaceutical manufacturing value chain.
Agentic AI adoption is limited by GxP exposure. AI that influences GxP-controlled processes is hard to deploy quickly without validation, auditability, and accountable human oversight.
CIOs cannot treat all digital knowledge as agent-ready. Agents need governed, current, version-controlled, and inspection-ready context, not just access to documents and systems.
Agentic AI exposes ownership gaps across the enterprise. No single function owns the full risk surface. CIOs need a governance model that clarifies who owns the agent, the data it uses, the decision it influences, the process it touches, and the evidence required to defend it.
Our Advice
Critical Insight
CIOs must make autonomy earn its place in pharma. Every agent that touches regulated work needs a defined decision role, approved knowledge sources, validated behavior, audit-ready evidence, and a named owner for the outcome; only then will agentic AI become scalable, defensible, and trusted.
Impact and Result
- Classify agentic AI opportunities. Each use case should be classified by GxP exposure, decision criticality, autonomy level, and required evidence.
- Define boundaries before selecting use cases. Each autonomy level should have clear rules for human review, auditability, validation, exception handling, and escalation.
- Build an agent-ready knowledge foundation. CIOs must ensure that data sources are current, version-controlled, permission-aware, and semantically connected through master data and process taxonomies.
Assess and Prioritize Agentic AI Use-Cases in Pharmaceutical Manufacturing
Build a controlled path from decision support to bounded autonomy across the pharmaceutical manufacturing value chain.
Analyst perspective
Embed decision intelligence into systems to drive real-time, closed-loop execution.
Pharmaceutical manufacturers have spent years digitizing laboratories, manufacturing sites, quality systems, clinical operations, regulatory workflows, and commercial engagement. These investments have improved visibility, documentation, and process efficiency, but they have not removed the central constraint: regulated decisions remain slow, evidence-heavy, and dependent on fragmented human coordination. AI can now summarize documents, retrieve records, and generate recommendations, but most pharmaceutical workflows still struggle to turn intelligence into timely, defensible action.
This is not only due to a lack of automation, but also the absence of trusted decision infrastructure across good practice-controlled processes. Procedures, batch records, deviations, lab results, regulatory commitments, supplier evidence, and commercial content often sit across disconnected systems, with different owners, controls, and levels of readiness. In this environment, speed without evidence creates risk, and autonomy without accountability is unacceptable.
Agentic AI introduces a new operating possibility: systems that can retrieve context, reason across workflows, coordinate next steps, and take bounded action under defined controls. In pharmaceutical manufacturing organizations, however, the opportunity is not unrestricted autonomy. It is governed autonomy. Agents must be classified by the decisions they influence, constrained by the authority they are given, grounded in approved knowledge, and monitored through audit trails, validation, and human override.
For CIOs, this makes agentic AI a leadership test rather than merely a technology deployment. The mandate is to determine where agents can safely assist, recommend, coordinate, or act across regulated workflows without weakening quality, compliance, patient safety, or accountability. The manufacturers that move fastest will be those that make autonomy defensible, repeatable, and trusted.
Shreyas Shukla
Principal Research Director, Industry
Info-Tech Research Group
Executive summary
Your Challenge
Agentic AI adoption is limited by GxP exposure. AI that influences GxP-controlled processes is hard to deploy quickly without validation, auditability, and accountable human oversight.
CIOs cannot treat all digital knowledge as agent-ready. Agents need governed, current, version-controlled, and inspection-ready context, not just access to documents and systems.
Agentic AI exposes ownership gaps across the enterprise. No single function owns the full risk surface. CIOs need a governance model that clarifies who owns the agent, the data it uses, the decision it influences, the process it touches, and the evidence required to defend it.
Common Obstacles
Validation approaches are not ready for agentic AI. Most pharma validation practices are built around predictable workflows, not agents that change behavior based on prompts, data, and model updates.
Master data and process taxonomies are inconsistent. Different systems may use different names for products, materials, sites, equipment, suppliers, tests, and quality events, which makes cross-system reasoning unreliable.
Accountability changes as the agent moves from assistive to autonomous. Ownership is simple when an agent summarizes information. It becomes harder when the agent recommends or triggers actions.
Info-Tech’s Approach
Classify agentic AI opportunities. Each use case should be classified by GxP exposure, decision criticality, autonomy level, and required evidence.
Define boundaries before selecting use cases. Each autonomy level should have clear rules for human review, auditability, validation, exception handling, and escalation.
Build an agent-ready knowledge foundation. CIOs must ensure that data sources are current, version-controlled, permission-aware, and semantically connected through master data and process taxonomies.
Info-Tech Insight
CIOs must make autonomy earn its place in pharma. Every agent that touches regulated work needs a defined decision role, approved knowledge sources, validated behavior, audit-ready evidence, and a named owner for the outcome; only then will agentic AI become scalable, defensible, and trusted.
Your Challenge
Agentic AI adoption is limited by GxP exposure.
Pharma CIOs cannot evaluate agentic AI as a normal productivity tool when it touches GxP-controlled workflows. The more an agent influences batch records, deviations, release decisions, lab investigations, distribution exceptions, regulatory commitments, or patient safety signals, the more it requires validation, auditability, access control, and accountable human oversight. This slows adoption because CIOs must prove not only that the agent works, but that it behaves reliably within regulated boundaries.
CIOs cannot treat all digital knowledge as agent-ready.
Pharma organizations may have digitized procedures, specifications, batch records, lab results, quality events, supplier files, and regulatory documents, but that does not make them usable by agents. Agents need current, approved, version-controlled, permission-aware, and context-rich knowledge to produce defensible recommendations. Without clean master data, consistent taxonomies, and clear evidence lineage, agents may retrieve the wrong information, miss critical context, or generate outputs that cannot be trusted in regulated workflows. Agentic AI exposes ownership gaps across the enterprise.
Agentic AI cuts across IT, quality, regulatory, manufacturing, lab, supply chain, data, cybersecurity, and legal teams, but no single function owns the full risk surface.
IT may own the platform, quality may own the process, regulatory may own commitments, and manufacturing may own execution, yet the agent may influence all of them at once. CIOs need a governance model that clarifies who owns the agent, the data it uses, the recommendation it makes, the decision it influences, and the evidence required to defend it.
In pharma, agentic AI adoption is constrained by whether regulated knowledge, decision rights, and GxP evidence are strong enough to make autonomy defensible.
Common Obstacles
Validation approaches are not ready for agentic AI.
Most pharma validation practices were designed for systems with predictable workflows, fixed rules, and repeatable outputs. Agentic AI may retrieve different context, generate different recommendations, interact with multiple systems, and change behavior when prompts, data sources, model versions, or workflow conditions change. This creates a validation problem because CIOs need to define the agent’s intended use, approved data sources, permitted actions, decision boundaries, test scenarios, exception paths, audit trail requirements, and monitoring controls before deployment. Without that, quality teams will slow or block adoption because they cannot defend how the agent behaves in a regulated process.
Master data and process taxonomies are inconsistent.
Agentic AI depends on reliable context that spans products, materials, active pharmaceutical ingredients, excipients, suppliers, sites, equipment, batches, tests, specifications, procedures, deviations, complaints, and regulatory commitments. These entities are often named, structured, and governed differently across enterprise, manufacturing, lab, quality, and regulatory systems. This makes cross-system reasoning unreliable. Until master data and process taxonomies are harmonized, agentic AI can assemble information quickly but still draw the wrong connections.
Accountability changes as the agent moves from assistive to autonomous.
Ownership is manageable when an agent only summarizes information or helps a user search controlled documents. It becomes much harder when the agent is influencing regulated decisions. This creates an accountability gap. IT may own the platform, but it cannot own the quality judgment. Quality may own the process but may not understand the model behavior. Manufacturing may own execution, but not the data pipeline. Regulatory may own commitments, but not the agent workflow. CIOs need a decision-rights model that changes with autonomy level, defining who owns the agent, the evidence it uses, the recommendation it makes, the action it triggers, and the failure modes it may introduce.
Agentic AI barriers cannot be removed one control at a time; pharma CIOs need to design one operating system for autonomy to account for validation, master data, process context, and decision rights.
Info-Tech’s Approach
Classify agentic AI opportunities.
Each opportunity should first be classified by GxP exposure, decision criticality, autonomy level, and required evidence. This forces the organization to distinguish between low-risk productivity support and workflows that could influence product quality, patient safety, batch disposition, regulatory commitments, or data integrity. This classification also prevents over-governance and under-governance. A document summarization agent should not be treated the same way as a deviation triage agent or a batch release readiness agent. By classifying opportunities upfront, CIOs can prioritize use cases that deliver value while matching the level of control to the level of regulated impact.
Define boundaries before selecting use cases.
CIOs should define what assistive, guided, conditional, and autonomous behavior means in a pharma context before deciding which use cases to pursue. Each autonomy level needs explicit rules for human review, auditability, validation, exception handling, escalation, and approval authority. A triage agent that routes general service tickets is very different from one that routes deviations, adverse event reports, or cold chain excursions. Boundaries should clarify what the agent can see, what it can recommend, what it can trigger, when it must stop, and when a human must take over.
Build an agent-ready knowledge foundation.
Agents cannot operate safely on fragmented or uncontrolled knowledge. CIOs must ensure that the data and content agents use is current, version-controlled, permission-aware, and semantically connected. This includes procedures, specifications, batch records, lab results, deviations, complaints, validation evidence, supplier records, regulatory commitments, and distribution data. The goal is to give agents reliable context that requires master data alignment, process taxonomies, metadata discipline, controlled document status, role-based access, evidence lineage, and clear rules for what sources are approved for agent use. Without this foundation, agents may work quickly but reason from incomplete, outdated, or misinterpreted information.
CIOs should make agentic AI deployable by turning every use case into a controlled design decision: classify the risk, bound the autonomy, and prove the agent is using trusted knowledge before it touches regulated work.
Info-Tech’s methodology for adopting agentic AI for pharmaceutical manufacturing workflows
Phase Steps | 1. Establish familiarity
| 2. Understand criteria
| 3. Evaluate use cases
| 4. Define value
| 5. Prioritize deployment
|
Phase Outcomes | Gain a shared understanding of agentic AI and where it could create value in the organization.Align on the organization’s value chain, the six value drivers, and the concept of agent autonomy. This creates a common vocabulary and ensures that all stakeholders evaluate opportunities through the same operational and strategic lens. | Gain clarity on how use cases will be evaluated and prioritized.Understand the scoring logic used in the tool, including how business impact and implementation feasibility are assessed. This ensures that use case evaluation is structured, comparable, and grounded in consistent criteria rather than subjective opinions. | Shortlist realistic agentic AI opportunities.Identify candidate use cases across the organization’s value stream and narrow them to a manageable evaluation set. The result is a curated list of opportunities that reflect real operational challenges and are suitable for structured prioritization. | Translate each use case into a clearly defined agent concept with measurable value.Assign value drivers, autonomy levels, and operational roles to each use case. This step ensures that opportunities are no longer abstract ideas but clearly defined agent capabilities with identifiable value and implementation characteristics. | Establish a prioritized roadmap of agentic AI initiatives.Map use cases on the impact versus feasibility matrix and identify the most practical starting points for deployment. The result is a phased implementation roadmap that balances value creation with organizational readiness and operational risk. |
Each step of this blueprint is accompanied by supporting deliverables to help you accomplish your goals
Agentic AI Use Case Selection Tool for Pharmaceutical Manufacturing
The tool helps CIOs evaluate where agentic AI should be applied across pharmaceutical manufacturing operations.
By systematically evaluating operational value, risk exposure, and governance readiness, the tool enables CIOs to identify where autonomy is appropriate, where it should remain constrained, and how adoption should be sequenced across the enterprise.
You get:
- A ready-to-use list of high-value AI use cases to support roadmap design, funding discussions, and implementation planning.
Outcomes
Gain a clear view of which use cases should be explored first.
Justify where autonomy should be introduced and where it must remain constrained due to safety, regulatory, or operational considerations.
Produce a practical sequence of pilots and deployments that align autonomy initiatives with your operational priorities and governance requirements.
Blueprint benefits
IT Benefits
- Identify where agentic AI is viable versus unsafe in regulated manufacturing. Separate human-reviewed use cases such as deviation triage, batch record review, and scheduling recommendations from actions that should not execute autonomously, such as batch release, quality disposition, or validated process changes.
- Define boundaries across manufacturing, quality, and enterprise systems. Establish where agents can observe, recommend, or trigger workflow actions across manufacturing execution, batch record, quality, lab, enterprise resource planning, warehouse, and supervisory control platforms.
- Enable controlled closed-loop execution across pharma workflows. Move from insight to recommendation to bounded action by routing deviations, flagging batch record exceptions, escalating cold chain excursions, or triggering maintenance work orders.
- Expose readiness gaps for real-time agentic AI. Highlight missing capabilities such as reliable equipment-state visibility, governed master data, version-controlled procedures, validated integrations, and audit-ready data lineage.
- Embed governance for agent-influenced decisions. Ensure every recommendation, escalation, and handoff is traceable, reviewable, explainable, and overridable where product quality, patient safety, data integrity, or regulatory commitments are affected.
- Design for fail-safe and degraded operation modes. Ensure plants can continue operating when agents fail, lose connectivity, produce uncertain outputs, or encounter incomplete context.
Business Benefits
- Accelerate regulated decision cycles without weakening compliance. Use agents to assemble evidence, triage exceptions, and coordinate reviews for deviations, batch records, lab investigations, supplier issues, and distribution excursions.
- Improve release, quality, and responsiveness through governed coordination. Reduce waiting time between manufacturing, quality, lab, maintenance, and supply chain teams while preserving accountable human decisions.
- Stabilize operations under volatility and constraint. Use agents to detect material shortages, equipment issues, environmental excursions, and schedule disruption early, then recommend controlled recovery actions.
- Enable cross-functional optimization, not siloed automation. Coordinate decisions across Plan, Source, Make, Quality, Release, and Deliver so local improvements do not create compliance, inventory, or service risk elsewhere.
- Increase consistency and repeatability of frontline decisions. Encode approved procedures, decision rules, and escalation logic into agents that support shifts, sites, and markets consistently.
- Improve resilience through faster exception response. Detect and route deviations, cold chain excursions, maintenance risks, and supply disruptions earlier, with documented escalation and recovery paths.
Insight summary
CIOs must make autonomy earn its place in pharma. Every agent that touches regulated work needs a defined decision role, approved knowledge sources, validated behavior, audit-ready evidence, and a named owner for the outcome; only then will agentic AI become scalable, defensible, and trusted.
Pharma is not short on potential agentic AI use cases; it is short on the control structures needed to scale them safely. As agents move closer to regulated decisions, CIOs must ensure autonomy is bounded by evidence, accountability, and Good Practice requirements before it becomes operational.
Build a controlled path from decision support to bounded autonomy across the pharmaceutical manufacturing value chain.
In pharma, agentic AI adoption is constrained by whether regulated knowledge, decision rights, and GxP evidence are strong enough to make autonomy defensible.Pharma CIOs are being asked to scale agentic AI in workflows where every decision must be explainable, traceable, and defensible. The challenge is determining where agents can safely influence regulated work without weakening evidence quality, decision ownership, or Good Practice controls.
Agentic AI barriers cannot be removed one control at a time. Pharmaceutical Manufacturing CIOs need to design one operating system for autonomy to account for validation, master data, process context, and decision-rights.
Agentic AI stalls when validation, master data, process context, and accountability are treated as separate problems. CIOs need to solve them together because an agent cannot be trusted in regulated workflows if its behavior, evidence, and ownership model are not aligned.
CIOs should make agentic AI deployable by turning every use case into a controlled design decision: classify the risk, bound the autonomy, and prove the agent is using trusted knowledge before it touches regulated work.
CIOs should make agentic AI deployable by turning each use case into a controlled design decision. Classify the regulated risk, define the agent’s boundaries, and ensure the agent can only act on governed, current, and traceable knowledge.
Measure the value of this blueprint
How can you measure the value of following Info-Tech’s approach?
The average IT consulting rate in the United States is $100 to $250 per hour.
The cost and effort involved in undertaking an AI use case selection and prioritization exercise varies depending on the size and scope of the project. The average price of a well-designed and executed AI use case selection exercise ranges from US$24,000 to US$40,000 at the lower end (assuming a two-member team charging the hourly average of US$100).
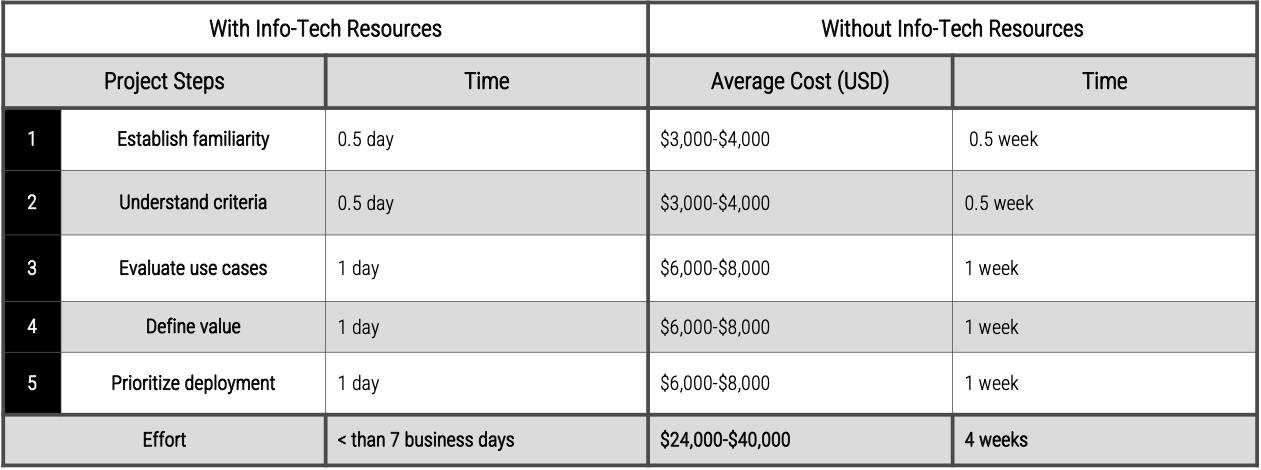
Source: “Understanding IT Consultant Cost…”, Wildnet Edge, 2026
This blueprint will accelerate your agentic AI use case prioritization exercise.
We include all the guidance, tools, and templates you need to implement this program successfully.
Reach out to advisory services for assistance as you work through the blueprint, or request a workshop engagement and let us do the heavy lifting.
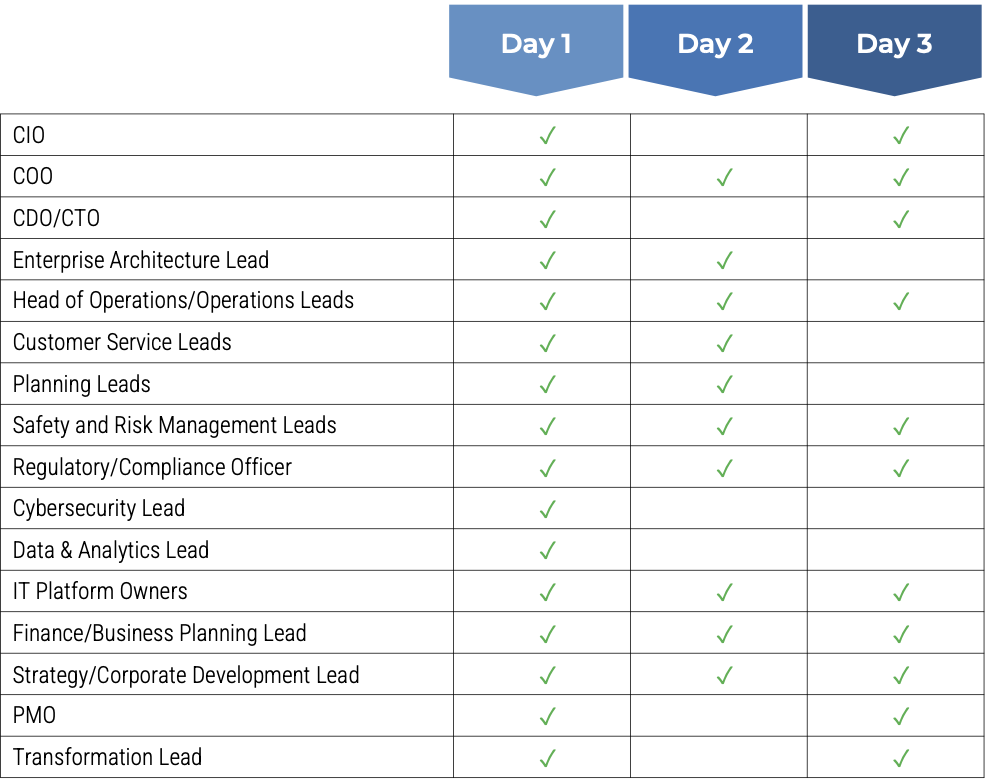
Recommended workshop participants
Before you proceed with the activities prescribed in the rest of this blueprint, do this…
- Download the accompanying Agentic AI Use Case Selection Tool for Manufacturing.Download the Agentic AI Use Case Selection Tool for Pharmaceutical Manufacturing
- Review related research for definitions and explanations on what agentic AI is, its maturity progression, common failure patterns, and everything else you need to get closer to implementing your first agentic AI pilot.Download the Design Your Agentic AI Prototype blueprint
- Review the key considerations section on how to effectively govern the use case selection process while keeping focus on structurally viable use case applications.Govern SelectionEnsure Structural Viability
CIOs should weigh two critical considerations when evaluating agentic AI solutions
Adoption is racing ahead, yet S&P Global finds 42% of companies abandoned most of their AI work in 2025, up from 17% a year earlier.1
CIOs must ensure that they have clarity on two points before proceeding:
Is it truly agentic?
Agentic validity: Is the solution actually reasoning, planning, using tools, and taking bounded actions, or is it a copilot, chatbot, analytics model, or workflow automation being marketed as agentic artificial intelligence?
Is it permissible?
Regulated permissibility: Is the organization allowed to use the agent in this workflow, given Good Practice requirements, data privacy, validation expectations, auditability, human accountability, and market-specific regulations?
80%+
of AI projects fail, twice the failure rate of IT projects that don’t involve AI.2
€35M / 7%
top EU AI Act penalty for a prohibited AI practice; up to €35M or 7% of global annual turnover, whichever is higher.3
Sources:
1 – “Generative AI…,” S&P Global, n.d.
2 – “The Root Causes…,” RAND Corporation, 2024
3 – “Article 99…,” EU Artificial Intelligence Act, 2025
Many “agentic AI” claims are overstated
Let’s look at some often-quoted agentic AI case studies and evaluate their claims
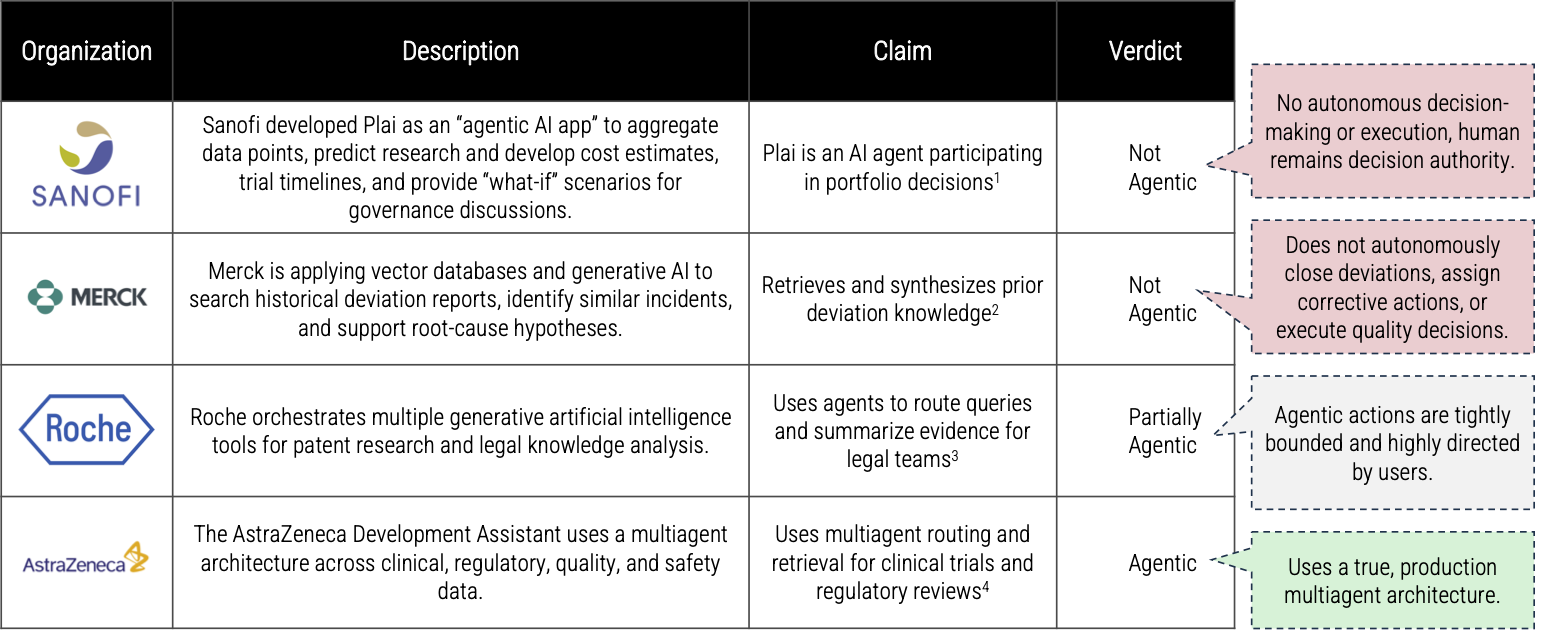
Sources:
1 – “AI Across the…”, Sanofi, 2026 2 – “MSD explores…”, AWS, 2025 3 - “Roche:..”, Dataiku, n.d. 4 - “Agentic AI Platform…”, ZenML, 2025
A step-by-step reality check
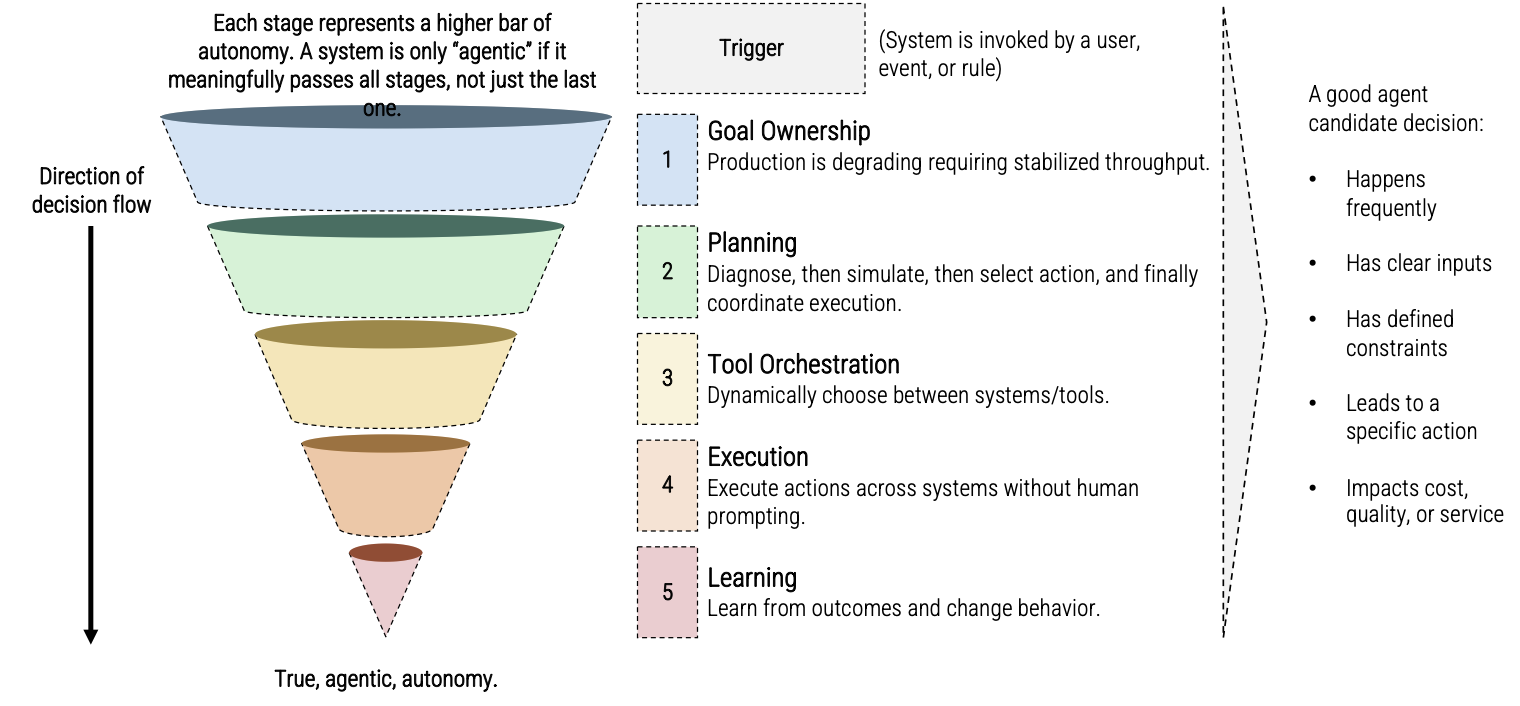
What is being labeled as agentic AI today is largely a combination of retrieval-augmented generation, workflow orchestration, and advanced automation, not true autonomous agents.
Stage | Question | Common Failure Patterns | What “True Agentic” Requires |
Goal Ownership | Does the system define or refine goals? | All systems are triggered by humans or predefined objectives | Self-directed objectives, not user-triggered tasks |
Planning | Does it break goals into multistep plans? | No dynamic decomposition of problems | Dynamic task decomposition |
Tool Orchestration | Does it select and use tools autonomously? | At best, routing between prebuilt tools | Cross-system decisioning, not pre-wired flows |
Execution | Does it act independently across workflows? | Works only within tightly engineered workflows | Minimal human triggering |
Learning & Adaptation | Does it improve behavior over time autonomously? | Improvements require human intervention | Closed-loop learning with feedback |
Determine whether a system is truly agentic vs. just automated AI
CIOs must ensure that agentic AI use cases are safe, controllable, and structurally viable before prioritizing value
Before evaluating business impact or feasibility, organizations must first determine whether a use case is structurally appropriate for agentic AI within a manufacturing environment. This step ensures that operational realities, safety constraints, and system dependencies are accounted for before any economic prioritization occurs.
Safety Criticality
- Does the use case impact human safety or asset integrity?
- Would an incorrect decision result in injury, damage, or regulatory breach?
High safety exposure requires human-in-the-loop or constrained autonomy.
Regulatory Sensitivity
- Is the process governed by strict regulatory, audit, or compliance requirements?
- Are decisions subject to traceability, explainability, or approval mandates?
High regulatory exposure limits full autonomy and requires audit controls.
Operational Centrality
- Is the use case part of core operational flow?
- Would failure disrupt primary service delivery or network performance?
Core operations require higher control and staged autonomy adoption.
Interdependency and Cascade Potential
- Does the use case interact with multiple systems, workflows, or downstream decisions?
- Can errors propagate across operational, network, customer, or financial systems?
High interdependency increases the need for coordination controls and supervision.
Reversibility and Containment
- Can decisions be easily reversed or corrected without downstream impact?
- Is there a clear mechanism to contain failures before they spread?
Low reversibility requires restricted autonomy and stronger guardrails.
Info-Tech Insight
High value does not justify high risk in manufacturing environments.
Even high-impact use cases must be constrained if they operate in safety-critical, highly regulated, or tightly coupled systems
Images have been generated using OpenAI’s GPT 5.4 large language model.
The compliance clock is already running
Many rules around governed and safe AI use are already in force now, while other regulations are fast emerging.
US/FDAFDA AI Guidance (2025)
EMERGING
Build a risk-based “context of use” credibility file now.1
21 CFR Part 11
IN FORCE
Agent actions on records need audit trails & human-bound e-signatures.2
Software Assurance (CSA)
IN FORCE
Focus validation effort on intended use, patient safety, product quality, and data integrity for AI tools.3
Privacy & Data
GDPR + DPIAIN FORCE
DPIA is mandatory for AI systems involving profiling, decision-making, or data processing.4
FRIA – high-risk AI
UPCOMING
Requires documented details of autonomous actions and human oversight measures.5
HIPAA/PIPEDA
IN FORCE
Agents must provide BAA and not train on patients’ data.6
EU AI Act
GPAI model dutiesIN FORCE
Providers must perform conformity assessments and deployers must ensure safe and compliant AI use.7
CE Marking
UPCOMING
Any high-risk AI system placed on the EU market or put into service must bear the CE mark.8
AI literacy (Art. 4)
IN FORCE
Mandates the skills, knowledge, and understanding required to make informed deployments of AI.9
Cyber & Global
NIS2 DirectiveIN FORCE
Agents should not operate with blanket permissions and require end-to-end tracing.10
Prompt-injection
EMERGING
Restrict type and nature of prompts and implement security content filters.11
MHRA/Health Canada/PMDA
EMERGING
Combination of GMLP principles and geo-specific requirements for developers.12, 13, 14
- In force (already deployed)
- Emerging (draft ready or being prepared)
- Upcoming (future deadline/2027 or later)
- “Considerations for…,” US FDA, 2025
- “What Is 21 CFR….,” Lab Manager, 2026
- “Agentic AI in…,” USDM Life Sciences, 2026
- “How to Conduct…,” Kiteworks, 2026
- “Article 27…,” EU Artificial Intelligence Act, 2026
- “AI Agents and…,” Cyber Defense Magazine, 2026
- “The roles of…,” Stephenson Harwood, 2024
- “CE Marking for…,” Dilaig, 2026
- “AI Literacy…,” Anekanta AI, n.d.
- “NIS2 Compliance…,” FALNOA, 2026
- “Prompt Injection…,” OWASP, n.d.
- “Pre-market guidance…,” Govt. of Canada, 2026
- “Machine learning medical…,” Gov.UK, 2024
- “Action Plan for…,” PMDA, 2025
Info-Tech Insight
Agentic autonomy shifts compliance from one-time validation to continuous, auditable oversight.
About Info-Tech
Info-Tech Research Group is the world’s fastest-growing information technology research and advisory company, proudly serving over 30,000 IT professionals.
We produce unbiased and highly relevant research to help CIOs and IT leaders make strategic, timely, and well-informed decisions. We partner closely with IT teams to provide everything they need, from actionable tools to analyst guidance, ensuring they deliver measurable results for their organizations.
What Is a Blueprint?
A blueprint is designed to be a roadmap, containing a methodology and the tools and templates you need to solve your IT problems.
Each blueprint can be accompanied by a Guided Implementation that provides you access to our world-class analysts to help you get through the project.
Need Extra Help?
Speak With An Analyst
Get the help you need in this 5-phase advisory process. You'll receive multiple touchpoints with our researchers, all included in your membership.
Guided Implementation 1: Establish familiarity
- Call 1: Review the capability map/value stream map.
- Call 2: Identify domains where agentic AI may create value.
Guided Implementation 2: Understand criteria
- Call 1: Understand agentic AI use cases across value stream domains.
- Call 2: Define the decision boundaries and expected operational outcomes.
Guided Implementation 3: Evaluate use cases
- Call 1: Evaluate fitment & risk scenarios.
Guided Implementation 4: Define value
- Call 1: Estimate value for each use case using metrics.
Guided Implementation 5: Prioritize deployment
- Call 1: Prioritize use cases by balancing value, risk, and readiness.
- Call 2: Develop a sequenced adoption roadmap.
Contributors
- Tim Smart, IT Director, Global Pharmaceuticals Company
- Steven Schmidt, Sr. Managing Partner, Info-Tech Research Group
- 1 Anonymous Contributor
