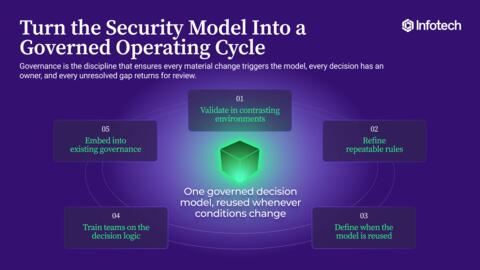
The tool records the rationale, evidence, ownership, approval status, and review dates associated with nonstandard decisions and links unresolved exposure to site-specific risk scenarios. It has specific sections to consolidate environment classifications, control decisions, baseline gaps, and risk definitions for leadership while also defining decision rights, escalation triggers, review cycles, and operating metrics.
Scalable OT Security Modeling Tool
Access this content by contacting one of our representatives for assistance.
Tags
OT security, operational technology security, OT cybersecurity, manufacturing OT security, manufacturing cybersecurity, industrial cybersecurity, industrial control system security, ICS security, factory cybersecurity, plant cybersecurity, multi-site OT security, multi-plant cybersecurity, enterprise OT security, scalable OT security, OT security strategy, OT security framework, OT security methodology, OT security operating model, OT security governance, OT governance framework, standardize controls, governed OT security, governed variation, control intent, security control intent, control implementation, OT control implementation, OT control applicability, OT control feasibility, global baseline controls, local security controls, OT control baseline, mandatory OT controls, compensating controls, control exceptions, baseline control gaps, governed adaptation, OT environment classification, operational technology environments, OT environment types, standard environment, OT constraint assessment, operational constraints, legacy OT systems, OT uptime sensitivity, safety-critical OT, vendor dependency, OT network constraints, OT change constraints, heterogeneous OT environments, mixed manufacturing environments, legacy and modern OT, brownfield OT security, unsupported OT systems, end-of-support OT risk, OT decision model, OT decision framework, OT decision logic, OT control decision process, OT escalation process, OT decision rights, cross-functional OT governance, IT OT governance, OT risk management, manufacturing cyber risk, operational cyber risk, inherent OT risk, residual OT risk, OT risk register, site-specific cyber risk, risk ownership, risk treatment, cyber risk acceptance, OT risk scenarios, OT governance lifecycle, OT exception governance, OT review cadence, enterprise OT reporting, OT security metrics, plant-level cyber visibility, manufacturing cybersecurity assessment, OT operating model validation, OT security rollout, reusable OT security model, OT security change triggers, OT security for new plants, OT security for acquisitions, OT security modernization, vendor remote access security, NIST, CSF 2.0, SP 800-82, SP 800-53 OT overlay, ISA IEC 62443, CIS Controls v8.1, MITRE ATT&CK for ICS, OT security standards, standards-informed OT security, outcome-based OT security, manufacturing CIO cybersecurity, manufacturing CISO strategy, industrial cyber resilience, cyber-resilient manufacturingShare on Social
Select Social Platform: