
Design a Viable OT Security Model for Mining Operations
Highlight enforceability to construct a viable and defensible security posture.
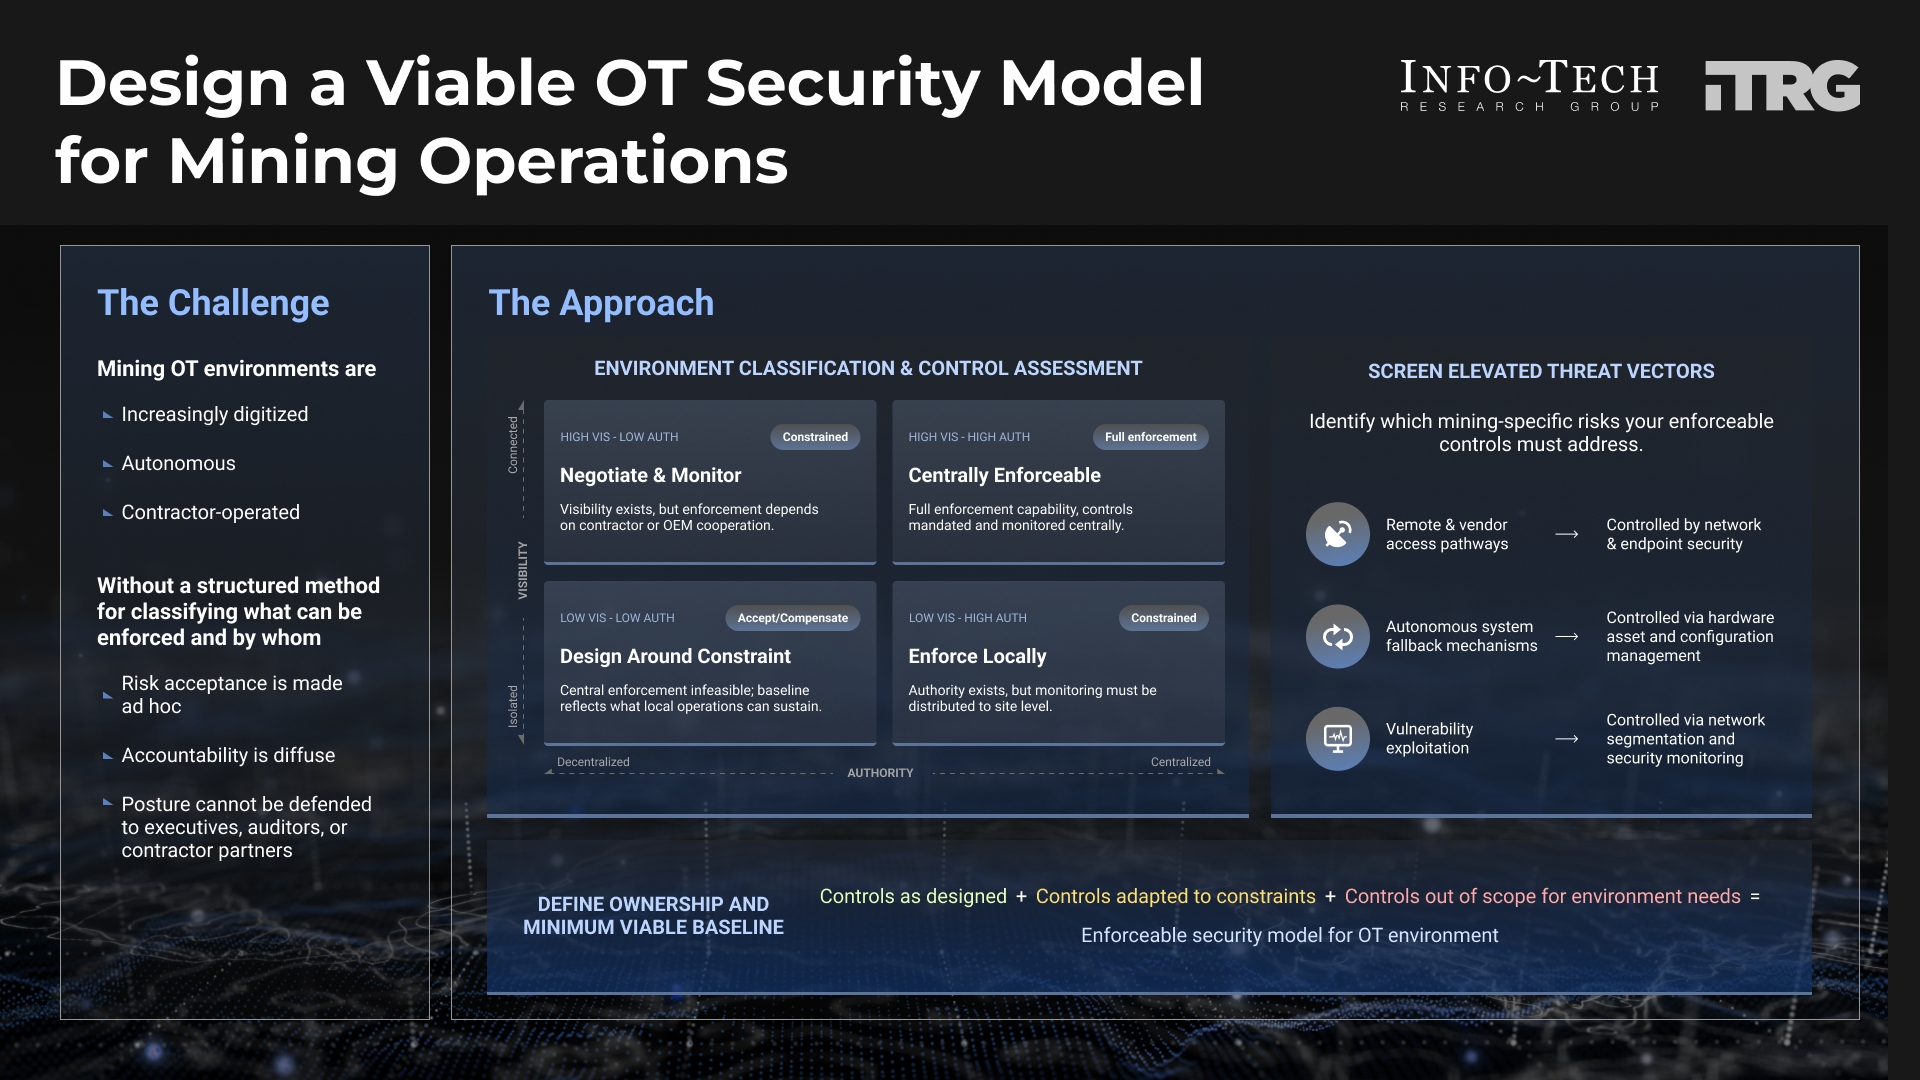
- Mining OT environments are increasingly digitized, autonomous, and contractor-operated, but security models are still built around what should be controlled rather than what can be controlled in actuality.
- Remote geography, intermittent connectivity, OEM-managed systems, and distributed operational authority mean that security intent and enforcement capability are rarely the same thing, and the gap between them is managed informally.
- Without a structured method for classifying what can be enforced and by whom, risk acceptance decisions are made ad hoc, accountability is diffuse, and security posture cannot be defended to executives, auditors, or contractor partners.
Our Advice
Critical Insight
- Existing OT security frameworks primarily speak to fixed infrastructure with centralized operations. They describe what controls should exist but provide no method for testing whether those controls can be enforced under constrained mining conditions.
- Enforceability gaps are consistently treated as a resourcing or maturity problem rather than a design problem, which means they persist even when they are recognized.
- IT security owns framework design; OT operations owns site constraints. Aligning these during design requires planning, effort, and coordination, which won’t get done without a mandate.
Impact and Result
- Classify your OT environments by visibility and authority to produce a characterization that reflects how your sites actually operate.
- Assess which controls can be enforced centrally, locally, or not at all, and screen that assessment against the threat vectors most elevated in constrained mining environments.
- Define a minimum viable security baseline that is documented, derived from your classification work, and defensible to executives, auditors, and partners.
About Info-Tech
Info-Tech Research Group is the world’s fastest-growing information technology research and advisory company, proudly serving over 30,000 IT professionals.
We produce unbiased and highly relevant research to help CIOs and IT leaders make strategic, timely, and well-informed decisions. We partner closely with IT teams to provide everything they need, from actionable tools to analyst guidance, ensuring they deliver measurable results for their organizations.
What Is a Blueprint?
A blueprint is designed to be a roadmap, containing a methodology and the tools and templates you need to solve your IT problems.
Each blueprint can be accompanied by a Guided Implementation that provides you access to our world-class analysts to help you get through the project.
Need Extra Help?
Speak With An Analyst
Get the help you need in this 3-phase advisory process. You'll receive multiple touchpoints with our researchers, all included in your membership.
Guided Implementation 1:
- Call 1: Scope requirements, objectives, and your specific challenges.
- Call 2: Segment site environments and identify environmental profiles.
Guided Implementation 2:
- Call 1: Validate environment threat vectors.
- Call 2: Determine control implementation priority by threat.
Guided Implementation 3:
- Call 1: Assign control ownership.
- Call 2: Finalize control implementation decisions & review baseline summary.